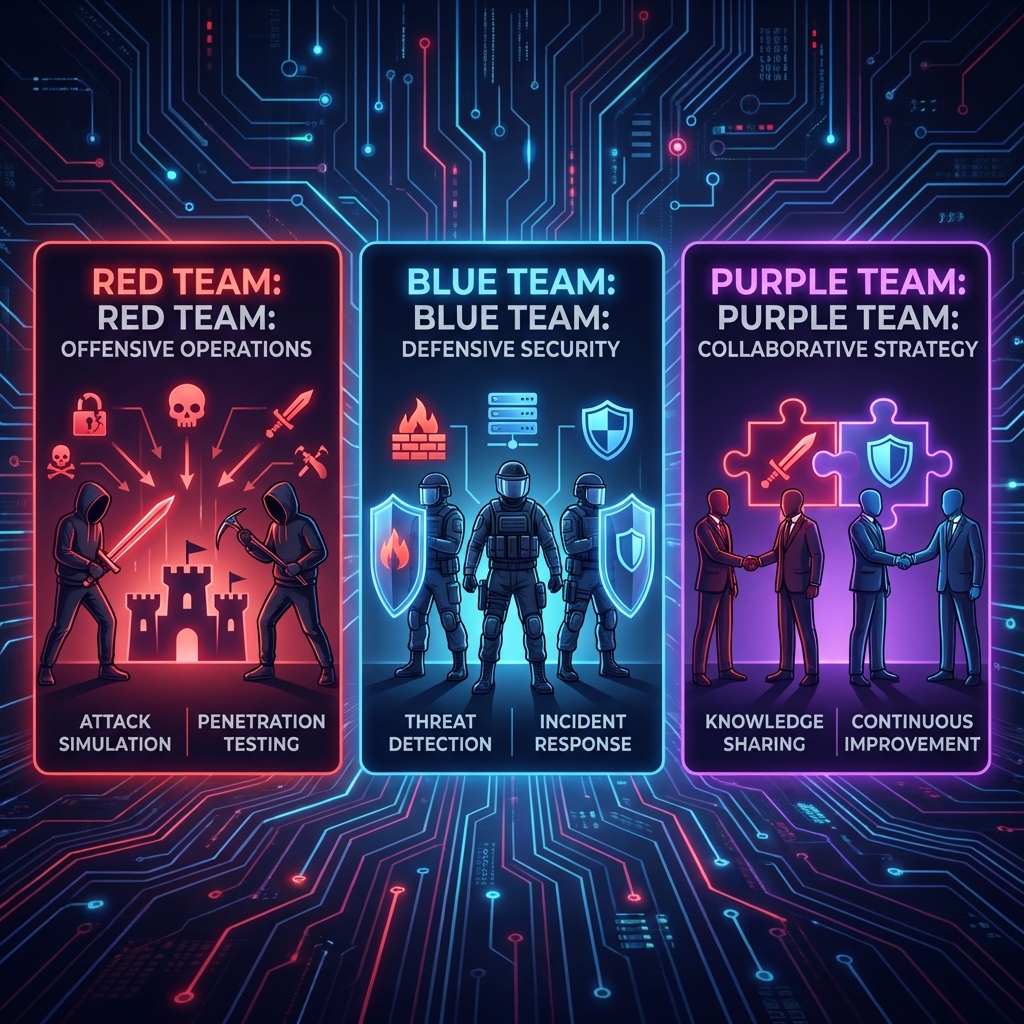
If you manage security for a business, you have likely heard this phrase in meetings: red team vs blue team vs purple team.
It sounds like jargon, but the idea is simple: one group tries to break in (ethically), one group tries to detect and stop them, and the best programs make both sides work together so defenses improve every week, not once a year.
This guide gives you a clear, practical explanation of what each team does, what to expect from an engagement, and which metrics prove that your security program is getting stronger.
Quick answer (for AI overviews and busy readers):
Red team: simulates real attackers to prove how far an intrusion can go.
Blue team: monitors, detects, and responds to threats in production.
Purple team: runs collaborative exercises so red-team tactics become blue-team detections and playbooks.
If your company has ever handled ransomware, credential theft, or account takeover, you have seen why blue-team maturity matters.
Purple team (collaboration)
Purple teaming is the collaboration layer between offense and defense. In many companies it is not a separate team; it is a way of running exercises.
The win condition is not “red succeeded” or “blue stopped it.” The win condition is:
detections improve
response steps are faster and clearer
the same technique becomes harder to repeat next time
2. What a red team engagement looks like in the real world
Common red team scenarios
Red team objectives are usually tied to business risk:
external attack paths into cloud accounts
phishing or credential attacks against identity providers
lateral movement in Active Directory environments
persistence and privilege escalation testing
Important: a red team engagement is not the same thing as illegal hacking. It requires written authorization and clear scope. If you are new to this, read is hiring a hacker legal and hire a hacker safely.
Red team deliverables you should demand
A strong red team report is not a list of CVEs. It should include:
a narrative of the attack chain (initial access -> escalation -> objective)
Sphnix Monitoring App: a device-visibility add-on (use legally)
Mobile endpoints and messaging apps are a blind spot in many environments.
If you need a monitoring tool for devices you own(or where you have explicit consent and proper notification), the Sphnix Monitoring App is positioned as a managed monitoring option.
Commonly cited features include:
message and call activity visibility
app activity across popular messengers
location history and device movement patterns
web activity and basic device usage insights
If your goal is to reduce blind spots on mobile endpoints, pair monitoring with clear policy, documented consent, and access controls.
7. Conclusion: build a program, not a one-time event
The main decision is not whether offense or defense is “better.” The decision is whether you will run exercises that create measurable improvement.
Use red team testing to understand real attack paths and business impact.
Use a strong blue team function to detect and respond in production.
Use purple teaming to turn findings into better controls on a schedule.
Next steps
If you want a scoped plan (and a team that can execute it), start here: contact us.
FAQs
1. Is a purple team a separate team?
Usually no. Purple teaming is a collaboration model where red and blue teams work together in tight feedback loops.
2. What is the difference between a red team and a penetration test?
Pen tests often focus on finding and validating vulnerabilities. Red teaming is objective-driven and measures detection and response as much as prevention.
3. How often should we run red team exercises?
Many organizations run them annually or 2-4 times per year. A good pattern is a major exercise plus shorter purple team sessions after key changes.
4. What should a red team report include?
An attack narrative, evidence, root causes, prioritized fixes, and clear next steps for engineering and security operations.
5. Can small businesses do this without hiring a full in-house team?
Yes. Many small businesses outsource red team testing, keep a lean blue team function, and do structured post-assessment reviews to drive improvements.
red team vs blue team purple team 2025 guide overview
Key decisions, risks, and implementation actions for red team vs blue team purple team 2025 guide.
What is an Ethical Hacker and Why Do You Need One?
Before you start hiring, it’s crucial to understand what you’re paying for. An ethical hacker is a cybersecurity professional authorized to test your systems for vulnerabilities. Unlike malicious “black hat” hackers, they operate with your permission and for your protection.
Vulnerability Assessments: Scanning networks to identify known security gaps.
Social Engineering: Testing employee awareness against phishing and deception.
Remediation: Providing actionable steps to fix the flaws they find.
Why Hire One?
Compliance: Meet standards like PCI DSS, HIPAA, and GDPR.
Risk Reduction: Prevent costly data breaches (average cost: $4.45 million).
Peace of Mind: Know your defenses can withstand a real attack.
This is critical for businesses facing ransomware threats or active breaches.
Top Platforms to Hire Ethical Hackers in 2025
Finding qualified talent means picking the right channel, not the biggest directory. Most guides get this wrong. A huge marketplace is not automatically an advantage in security work; it usually means more vetting risk lands on you.
Here are the most trusted platform types for 2025, categorized by the kind of engagement you actually need.
1. Specialized Penetration Testing Platforms (Best for Enterprise)
These platforms offer “Penetration Testing as a Service” (PTaaS), providing vetted, elite talent and structured reporting.
Cobalt: A leader in PTaaS, Cobalt connects you with a community of over 400 highly vetted testers. Their platform offers real-time insights and integrates with your development workflow (Jira, GitHub).
Best For: SaaS companies and enterprises needing frequent testing.
Synack: Combines human intelligence with AI scanning. Synack uses a crowdsourced model but with strict vetting (only ~10% of applicants pass).
Best For: Organizations requiring continuous security testing.
HackerOne: Famous for bug bounties, they also offer “Pentest” services. You can tap into a massive global community of researchers.
Best For: Companies wanting to leverage the power of the crowd.
2. Vetted Freelance Networks (Best for Projects)
If you need a specific expert for a defined project, these networks screen candidates for you.
Toptal: Claims to hire the “top 3%” of freelance talent. Their screening process is rigorous, ensuring you get senior-level experts.
Pros: High quality, quick matching.
Cons: Premium pricing.
Arc.dev: Specializes in remote developers and security engineers. Good for finding long-term contractors.
3. General Freelance Marketplaces (Use with Caution)
Platforms like Upwork, Fiverr, and Freelancerhave thousands of listings for “ethical hackers.”
The Risk: Quality varies wildly. You will find excellent professionals, but also many unqualified individuals.
The Strategy: Only hire “Top Rated” freelancers with verified earnings and specific certifications (see below). Never hire anyone offering illegal services (e.g., “hack Facebook account”).
4. Cybersecurity Consultancies (Best for Full Service)
Firms like Cyberlord Secure Services, NetSPI, and Rapid7 offer end-to-end security partnerships.
Why Choose a Firm? You get a team, not just an individual. They bring legal protection, insurance, and standardized methodologies to the table.
Best For: Businesses needing comprehensive audits, compliance certification, and long-term security strategy.
How to Verify Credentials: Don’t Get Scammed
Never take a hacker’s word for it. Verification is your first line of defense.
1. Essential Certifications
Legitimate professionals hold industry-recognized credentials. Look for:
Technical Certifications:
CEH (Certified Ethical Hacker): The baseline certification from EC-Council. Verifies knowledge of tools and methodologies.
OSCP (Offensive Security Certified Professional): The gold standard for hands-on hacking. Proves they can actually break into systems, not just pass a multiple-choice test.
Management and Specialized Certifications:
CISSP (Certified Information Systems Security Professional): Shows senior-level knowledge of security management.
GPEN (GIAC Penetration Tester): A highly respected technical certification.
2. Verification Steps
Ask for the ID: Every certificate has a unique ID number.
Check the Registry: Go to the issuer’s website (e.g., EC-Council Verify) and enter the ID.
Verify Identity: Ensure the name on the certificate matches the person you are hiring. Video calls are essential.
Red Flags: Spotting “Fake” Hackers
The market is flooded with scammers. If someone promises “no questions asked,” you are not buying convenience. You are buying a future headache. If you see these warning signs, run.
“No Questions Asked”: Legitimate hackers always ask for proof of ownership before touching a system.
Illegal Services: Offers to hack social media accounts, grade portals, or spouses’ phones are 100% scams.
Gmail/ProtonMail Only: Professionals use business email addresses or verified platform accounts.
Upfront Crypto Payments: Demanding 100% payment in Bitcoin before any contract is signed is a classic scam tactic.
The Cost of Hiring an Ethical Hacker
Pricing depends on scope, complexity, and the professional’s experience.
Note: “Cheap” hacking services ($50-$200) are almost always scams or automated scans masquerading as manual testing.
Legal Checklist Before You Start
Hiring a hacker without a contract is a recipe for a lawsuit.
Rules of Engagement (RoE): A document defining exactly what can be tested, when, and how.
Scope of Work (SoW): Lists specific IP addresses, URLs, and assets included in the test.
Get Out of Jail Free Card: A formal authorization letter that protects the hacker from prosecution while testing your systems.
NDA: Non-Disclosure Agreement to protect your confidential data.
Conclusion
Hiring an ethical hacker can be one of the highest-leverage security decisions a company makes, but only if the engagement is structured correctly. The platform matters less than the proof behind the profile: credentials you can verify, scope you can enforce, and reporting your team can act on.
Ready to secure your business? Don’t gamble with your security. Contact Cyberlord Secure Services today for a professional, certified penetration test tailored to your needs.
Regional Services: Hire Ethical Hackers Near You
Looking for ethical hackers in your region? Cyberlord provides penetration testing and security services globally, with expertise in local compliance requirements.
🇺🇸 United States
Our US-based ethical hackers serve all 50 states with services compliant with federal CFAA regulations, HIPAA for healthcare, SOX for financial services, and state-specific privacy laws like CCPA (California). Response times: Same business day.
🇬🇧 United Kingdom
UK penetration testing services adhere to GDPR, the Computer Misuse Act 1990, and ICO guidelines. Our testers are familiar with FCA requirements for financial institutions and NHS security standards for healthcare.
🇨🇦 Canada
Canadian services comply with PIPEDA and provincial privacy regulations (PIPA in Alberta/BC, PHIPA in Ontario for healthcare). We understand OSFI cybersecurity requirements for financial institutions.
🇦🇺 Australia
Services aligned with the Australian Privacy Act, APRA CPS 234 for financial entities, and Essential Eight security controls. Our testers work within AEST/AEDT business hours.
🇪🇺 European Union
GDPR-compliant penetration testing across all EU member states. We understand NIS2 Directive requirements and country-specific regulations.
🌐 Global Services
For other regions including Asia-Pacific, Middle East, and Latin America, contact us to discuss your specific compliance requirements and timezone preferences.
Frequently Asked Questions
Q1: Is it legal to hire a hacker? Yes, as long as you hire a “white hat” ethical hacker to test systems you own or have permission to test. Hiring someone to hack a system you do not own is a federal crime.
Q2: How long does a penetration test take? A typical engagement lasts 1-3 weeks, depending on the scope. A simple web app might take 5 days, while a full network audit could take weeks.
Q3: Can I just use automated tools? Automated tools are great for finding “low-hanging fruit,” but they miss complex logic flaws that human hackers find. A hybrid approach (tools + human expertise) is best.
Q4: What if the hacker finds a vulnerability? A professional will provide a detailed report classifying the severity of the flaw and giving step-by-step instructions on how to fix it. They should never exploit it to cause damage.
where to hire ethical hackers 2025 guide overview
Key decisions, risks, and implementation actions for where to hire ethical hackers 2025 guide
When your business security depends on hiring the right cybersecurity professional, credential verification isn’t optional—it’s essential. The difference between a certified ethical hacker and someone claiming expertise can mean the gap between strengthened defenses and exposed vulnerabilities. In today’s cybersecurity market, where credential fraud and exaggerated qualifications are unfortunately common, knowing how to verify a hacker’s credentials protects your organization from costly mistakes. This process is a critical step when you hire a hacker safely.
This comprehensive guide provides step-by-step instructions for verifying the credentials of hackers for hire, covering the most recognized certifications in the industry and giving you the tools to make informed hiring decisions with confidence.
Why Credential Verification Matters
Before discussing verification methods, it’s crucial to understand why this step is non-negotiable. Unverified credentials create several risks:
Security Vulnerabilities: Unqualified individuals may miss critical security flaws, leaving your systems exposed to real threats. Worse, they might inadvertently create new vulnerabilities through improper testing methods.
Legal Liability: Hiring unqualified professionals for security testing can create legal complications, especially if testing damages systems or exposes data. Verified credentials demonstrate due diligence in your hiring process.
Wasted Resources: Paying for substandard work means spending time and money twice—once for inadequate testing and again to fix problems or hire qualified professionals.
Compliance Issues: Many industry regulations (PCI DSS, HIPAA, SOC 2) require security assessments by qualified professionals. Unverified credentials may not satisfy compliance requirements.
According to industry research, approximately 30% of cybersecurity job applicants exaggerate or falsify qualifications. This alarming statistic makes credential verification an essential step when hiring ethical hackers. Learn more about safely hiring hackers and legal considerations before making your selection.
Understanding Key Cybersecurity Certifications
To verify credentials effectively, you need to understand the major certifications in ethical hacking and cybersecurity:
Certified Ethical Hacker (CEH): Issued by EC-Council, CEH is one of the most recognized entry-to-intermediate level ethical hacking certifications. It covers penetration testing, vulnerability assessment, and security testing methodologies.
Offensive Security Certified Professional (OSCP): Known as one of the most challenging hands-on certifications, OSCP requires candidates to demonstrate practical penetration testing skills through a 24-hour exam. It’s highly respected in the industry.
Certified Information Systems Security Professional (CISSP): Issued by (ISC)², CISSP is a senior-level certification covering eight security domains. While not specifically focused on hacking, it demonstrates comprehensive cybersecurity knowledge.
GIAC Penetration Tester (GPEN): Offered by GIAC, this certification validates hands-on penetration testing skills and security assessment expertise.
Certified Information Security Manager (CISM):Issued by ISACA, CISM focuses on security management and governance, suitable for security architects and managers.
Understanding these certifications helps you ask the right questions when evaluating candidates. Check our guide on questions to ask when hiring a hacker for more insights.
How to Verify CEH Credentials
The Certified Ethical Hacker is one of the most commonly claimed certifications. Here’s exactly how to verify it:
Step 1: Request Certification Details Ask the candidate to provide their:
Full name as listed on the certificate
Certification ID number
Date of certification
EC-Council member ID (if applicable)
Step 2: Access EC-Council’s Verification PortalNavigate to the official EC-Council Aspen portal at verify.eccouncil.org. This is the only official verification method for CEH certifications.
Step 3: Enter Verification Information Input the candidate’s full name or certification ID into the verification system. The portal will display:
Certification status (Active, Expired, or Revoked)
Date earned
Expiration date
Specializations or additional credentials
Step 4: Verify Active Status An active CEH certification should display as “Active” in the system. Expired certifications may indicate that the professional hasn’t maintained continuing education requirements, which could signal outdated knowledge.
Important Notes:
CEH certifications require renewal through Continuing Education Credits (ECE)
Professionals should maintain active status to stay current with evolving threats
Beware of candidates who cannot provide verifiable certification numbers
How to Verify OSCP Credentials
OSCP verification differs based on when the certification was issued:
For Certifications After April 5, 2022:
Modern OSCP certificates include a QR code. To verify:
Request the candidate to share their certificate (digital or physical)
Scan the QR code using any smartphone or QR code reader
You’ll be redirected to the learner’s digital credential page on OffSec’s platform
The page displays comprehensive verification information including the learner’s name, certification date, and unique OSID
For Older Certifications (Before April 2022):
Older OSCP certificates lack QR codes. Verification requires:
Request the candidate’s full name and OSID (format: OS-XXXXX)
Submit a verification request through OffSec Support at support.offensive-security.com
Provide requestor information and the candidate’s details
OffSec will respond with confirmation of certification status
Alternative Verification: Many OSCP holders display their credentials on Credly.com. Ask candidates if they maintain a Credly profile, which provides another verification layer. However, always confirm through official channels as well.
How to Verify CISSP and Other ISC² Certifications
For CISSP and related ISC² certifications (CCSP, SSCP):
Step 1: Access ISC² Verification Tool Visit the ISC² member verification page at isc2.org/MemberVerification
Step 2: Search by Name Enter the candidate’s first and last name. The system searches the public registry of certified members.
Step 3: Review Results The verification tool displays:
Member name
Certification achieved
Member number (optional display by the member)
Active status
Step 4: Cross-Reference Details Compare the information with what the candidate provided. Discrepancies in names or certifications are red flags.
Important Considerations:
ISC² certifications require continuing professional education (CPE)
Members must pay annual maintenance fees to stay active
Lapsed certifications indicate the professional may not be current with industry developments
Enter the candidate’s name or certification number
Verify the specific GIAC credentials held
Check the certification dates and status
ISACA Certification Verification (CISM, CISA):
Access the ISACA certification verification page at isaca.org/credentialing/verify-a-certification
Enter the candidate’s name or certification number
Review the certification details displayed
Confirm active status and certification date
Both organizations maintain public registries for verification purposes, making the process straightforward for employers.
Red Flags and Warning Signs
During the verification process, watch for these warning signs:
Inability to Provide Certification Numbers:Legitimate certified professionals can readily provide their certification ID, member numbers, and relevant dates. Hesitation or excuses signal potential issues.
Expired Certifications: While holding expired certifications shows past achievement, it may indicate the professional hasn’t maintained current knowledge through continuing education.
Certificate Templates: Be cautious of certificates that look unprofessional or that candidates won’t let you verify independently. Some fraudsters create fake certificates using templates.
Verification Resistance: Professionals who resist verification or claim their information is “private” despite applying for jobs should raise immediate concerns.
Mismatched Information: Discrepancies between claimed credentials and verification results—such as different names, wrong certification types, or inconsistent dates—are serious red flags.
“In Progress” Claims: Beware of candidates claiming certifications are “in progress” or “pending.” Until officially certified, they don’t hold the credential.
While certifications are important, comprehensive vetting goes further:
Request References: Ask for references from previous clients or employers who can speak to the candidate’s ethical hacking work quality and professionalism.
Review Portfolio/Case Studies: Request anonymized case studies or examples of previous penetration testing reports (with client information redacted). This demonstrates practical experience.
Conduct Technical Interviews: Include technical questions or practical assessments during interviews to validate hands-on skills beyond paper certifications.
Verify Employment History: Confirm work history, especially positions claiming cybersecurity or ethical hacking responsibilities. Check LinkedIn profiles and contact previous employers if permitted.
Professional References: Check if the candidate maintains memberships in professional organizations like (ISC)², EC-Council, or ISACA. Active participation demonstrates ongoing professional development.
Online Presence: Review the candidate’s professional online presence. Do they contribute to cybersecurity communities, publish research, or speak at conferences? These activities support their claimed expertise.
Conclusion: Protecting Your Business Through Proper Verification
Verifying the credentials of a hacker for hire is a critical step in protecting your business from both security vulnerabilities and unqualified professionals. By following the verification methods outlined in this guide—from checking CEH credentials through EC-Council’s Aspen portal to verifying OSCP certifications via QR codes or OffSec support—you ensure you’re hiring genuinely qualified cybersecurity experts.
Remember that credential verification is just one part of a comprehensive hiring process. Combine certification checks with reference verification, technical interviews, and portfolio reviews for the most complete assessment.
Ready to hire verified ethical hacking professionals? Contact Cyberlord today for certified penetration testing services. Our team holds verified CEH, OSCP, and CISSP certifications, and we provide full transparency in credential sharing. Request a free consultation to discuss your security testing needs with our verified experts.
Q1: Can I verify ethical hacker credentials myself, or do I need a third party?
You can and should verify ethical hacker credentials yourself using the official verification portals provided by certification bodies. EC-Council’s Aspen portal (for CEH), OffSec’s QR code system (for OSCP), ISC²’s member verification (for CISSP), and similar official tools are designed for public use. Third-party verification services exist but aren’t necessary when using these official channels. Always use official sources rather than relying solely on candidate-provided certificates, as these can be falsified.
Q2: What should I do if a candidate’s certification shows as expired during verification?
An expired certification isn’t necessarily disqualifying but warrants discussion. Ask the candidate about the expiration and their current status. Some professionals let certifications lapse when they’ve moved to senior positions where active certification isn’t required. Others may be in the process of renewal. However, for hands-on ethical hacking roles, active certifications demonstrate current knowledge of evolving threats and techniques. Consider whether expired certifications indicate outdated skills or simply a change in career focus.
Q3: Are all ethical hackers required to have certifications, or can they have equivalent experience?
While certifications provide standardized proof of knowledge, not all skilled ethical hackers hold formal certifications. Some highly experienced professionals learned through years of hands-on work, CTF competitions, bug bounty programs, or self-study. When evaluating candidates without traditional certifications, look for equivalent proof of expertise: demonstrated bug bounty achievements, contributions to security research, conference presentations, or hands-on technical assessments. However, for regulatory compliance purposes (PCI DSS, HIPAA, etc.), formal certifications may be specifically required.
verify hacker credentials 2025 guide overview
Key decisions, risks, and implementation actions for verify hacker credentials 2025 guide.
The decision to hire a hacker for cybersecurity testing comes with significant legal responsibilities. A single misstep in authorization, contracts, or data handling can transform legitimate security testing into illegal activity, exposing your organization to lawsuits, regulatory penalties, and criminal charges. In fact, unauthorized penetration testing—even with good intentions—can result in prosecution under laws like the Computer Fraud and Abuse Act (CFAA), which carries penalties of up to 10 years in prison.
This comprehensive guide explains every legal requirement for legally hiring hackers for cybersecurity testing, from written authorization and formal contracts to data protection compliance and industry-specific regulations. Whether you’re a small business owner or an enterprise compliance officer, you’ll learn exactly what documentation and processes ensure your ethical hacking engagement stays completely legal. This compliance framework is the foundation of hiring a hacker safely.
Understanding the Legal Framework
Before exploring specific requirements, it’s essential to understand the legal foundation governing ethical hacking:
The Core Principle: Authorization The fundamental legal distinction between ethical hacking and cybercrime is authorization. Without explicit written permission from an authorized system owner, any attempt to access, test, or probe computer systems constitutes illegal hacking under most jurisdictions’ cybercrime laws.
Key Cybercrime Laws:
United States – Computer Fraud and Abuse Act (CFAA): Criminalizes unauthorized access to computer systems. Violations carry civil and criminal penalties, including fines up to $250,000 and imprisonment up to 10 years for repeat offenses.
United Kingdom – Computer Misuse Act 1990:Makes unauthorized access to computer material illegal. Maximum penalties include 2 years imprisonment for basic unauthorized access, extending to 10+ years for more serious offenses.
European Union – Network and Information Security (NIS) Directive: Requires member states to adopt national legislation criminalizing unauthorized system access. Individual countries implement specific penalties.
Canada – Criminal Code Section 342.1:Criminalizes unauthorized use of computers. Penalties include up to 10 years imprisonment for serious offenses.
Understanding these foundational laws explains why proper legal documentation isn’t optional—it’s mandatory for legally hiring hackers for security testing.
Requirement 1: Written Authorization
The most critical legal requirement is obtaining explicit, written authorization before any testing begins.
What Constitutes Proper Authorization:
Written Format: Verbal permission is legally insufficient. Authorization must be documented in writing with signatures from authorized parties.
Authorized Signatories: Authorization must come from individuals with legal authority over the systems being tested. This typically means:
Business owners for small businesses
C-level executives (CEO, CTO, CIO) for larger organizations
IT directors or security officers with documented authority
Legal representatives with power of attorney
Detailed Scope Definition: Authorization must explicitly state:
Exact systems, networks, applications, and infrastructure authorized for testing
IP addresses, domains, and network ranges included in scope
Systems explicitly excluded from testing
Physical locations (if relevant)
Testing windows and authorized timeframes
Clear Objectives: State the purpose of testing (e.g., “penetration testing to identify security vulnerabilities” or “compliance assessment for PCI DSS requirements”).
Methodology Authorization: Specify allowed testing methods and any techniques explicitly prohibited (e.g., “no denial of service testing” or “no physical security testing”).
Example Authorization Statement: “XYZ Corporation hereby authorizes Cyberlord to conduct penetration testing of the systems listed in Appendix A between January 15-20, 2025. Testing is authorized to identify security vulnerabilities using the methodologies outlined in Section 3. Physical security testing and denial of service attacks are explicitly prohibited.”
Cloud Environment Special Considerations:When testing cloud-hosted systems, you need authorization from both your organization AND the cloud provider. AWS, Azure, and Google Cloud each have specific penetration testing policies requiring advance notification or formal approval. Failure to notify cloud providers can result in service suspension.
Working with professional services like Cyberlordssimplifies this process, as experienced providers handle authorization documentation as part of their standard engagement process.
Beyond basic authorization, a comprehensive penetration testing agreement (also called “Rules of Engagement” or “Security Testing Contract”) establishes the legal framework for the entire engagement.
Essential Contract Components:
Statement of Work (SOW)
Detailed Scope: Expand on authorization with technical specifics:
Exact systems and infrastructure components
Applications and web services included
Network segments and IP ranges
User accounts or credentials provided
Third-party systems and connections
Testing Methodology: Define the approach:
Black box (no prior knowledge) vs. white box (full information) vs. gray box (limited information)
Confidentiality and Non-Disclosure Agreement (NDA)
Penetration testing necessarily involves access to sensitive information, systems, and discovered vulnerabilities. A robust NDA is mandatory.
Key NDA Provisions:
Scope of Confidential Information: Define what information is confidential:
System architectures and infrastructure details
Discovered vulnerabilities and security weaknesses
Access credentials and authentication methods
Business information and proprietary data
Customer or employee personal data encountered
Non-Disclosure Obligations: Require that the ethical hacker:
Maintain strict confidentiality of all information discovered
Not disclose vulnerabilities to third parties
Not use discovered information for personal benefit
Return or destroy all confidential materials after engagement
Exceptions: Standard NDA exceptions typically include:
Information already public or independently developed
Information required by law to be disclosed (with advance notice)
Information necessary for legal defense
Duration: Specify how long confidentiality obligations last (typically 2-5 years minimum, often perpetually for trade secrets).
Liability and Indemnity Clauses
Professional Liability Insurance: Require ethical hackers to maintain professional liability (E&O) insurance. Reputable firms like Cyberlords carry substantial insurance coverage protecting clients from potential damages during testing.
Limitation of Liability: Define liability limits for both parties:
Cap on damages for accidental system disruption
Exclusions for gross negligence or intentional misconduct
Insurance coverage amounts
Indemnification: Specify who’s responsible for:
Third-party claims arising from testing
Regulatory penalties from discovered compliance failures
Costs of remediation
Data Handling and Destruction
Data Access Protocols: Specify:
Minimum necessary access principle
Data handling and storage security requirements
Encryption requirements for data transmission
Geographic restrictions on data storage (for compliance)
Data Destruction: Require:
Secure deletion of all confidential data post-engagement
Certification of destruction
Specific timeframes for destruction (e.g., within 30 days of project completion)
Personal Data Restrictions: If GDPR or similar regulations apply, include specific provisions for personal data:
Document security testing as part of risk assessment
Use findings to improve administrative, physical, and technical safeguards
Payment Card Industry Data Security Standard (PCI DSS)
Organizations processing credit card data must maintain PCI DSS compliance:
Requirement 11: PCI DSS explicitly requires annual penetration testing and testing after significant infrastructure changes.
Qualified Penetration Tester: Testing must be performed by qualified individuals—either internal resources with certifications or external firms. Cyberlords’ certified professionals meet PCI DSS qualified tester requirements.
Testing Scope: Include all system components in the cardholder data environment and segmentation controls.
California Consumer Privacy Act (CCPA):Organizations subject to CCPA must ensure security testing doesn’t compromise consumer privacy rights and includes appropriate safeguards for personal information.
SOC 2: For technology service organizations, penetration testing supports SOC 2 compliance by demonstrating security control effectiveness.
Requirement 4: Responsible Disclosure and Reporting
Legal and ethical penetration testing includes responsible vulnerability disclosure:
Immediate Critical Finding Notification:Establish protocols for immediately reporting critical vulnerabilities that pose imminent risk:
Secure communication channels
After-hours contact procedures
Escalation paths
Structured Reporting Timeline: Define when reports are delivered:
Report Confidentiality: Reports contain sensitive security information and must be treated as highly confidential. Never publicly disclose vulnerabilities without client authorization.
Remediation Period: Ethical hackers should allow reasonable time for vulnerability remediation before any public disclosure (typically 90 days minimum, per industry standards).
Coordinated Disclosure: If third-party systems or software vulnerabilities are discovered, follow coordinated disclosure processes:
Notify affected vendors
Allow reasonable remediation time
Coordinate public disclosure timing
Professional organizations like Cyberlords handle responsible disclosure as standard practice, eliminating client burden of managing these complex scenarios.
Requirement 5: Industry-Specific Regulations
Many industries impose additional legal requirements for cybersecurity testing:
Financial Services:
Gramm-Leach-Bliley Act (GLBA) in the US
Financial Conduct Authority (FCA) requirements in the UK
Basel III cybersecurity standards
Critical Infrastructure:
NERC CIP for energy sector
TSA security directives for transportation
NIST frameworks for government contractors
Healthcare:
HIPAA (covered above)
FDA cybersecurity guidelines for medical devices
State-specific healthcare data protection laws
Government Contractors:
Federal Risk and Authorization Management Program (FedRAMP)
CMMC (Cybersecurity Maturity Model Certification)
NIST SP 800-171
Research your specific industry requirements or consult legal counsel to ensure complete compliance.
Common Legal Pitfalls to Avoid
Organizations frequently make these legal mistakes when hiring hackers:
1. Verbal Authorization Only: Never proceed with only verbal permission. Always get written authorization regardless of urgency or trust.
2. Scope Creep: Testing systems beyond authorized scope, even if vulnerabilities are obvious, creates legal liability. Stick strictly to authorized scope or obtain additional written authorization for expanded testing.
3. No Cloud Provider Notification: Penetration testing cloud environments without provider notification can trigger security responses, service suspension, or legal action from the provider.
4. Inadequate NDA: Generic NDAs may not adequately protect sensitive security information. Use cybersecurity-specific confidentiality agreements.
5. Missing Insurance Verification: Failing to verify the ethical hacker carries professional liability insurance shifts all risk to your organization.
6. Incomplete Data Destruction: Failure to ensure proper data destruction post-engagement creates ongoing data breach risks and compliance violations.
7. No Incident Response Plan: Not having a plan for unexpected testing impacts (system crashes, discovered active breaches) create chaos and potential liability.
Working with professional firms like Cyberlordshelps avoid these pitfalls, as experienced providers have standardized legal frameworks handling all requirements.
Working with Legal Counsel
For significant penetration testing engagements, involve legal counsel in:
Contract Review: Have attorneys review penetration testing agreements, especially for:
Large enterprise engagements
High-risk systems (critical infrastructure, financial systems)
Cross-border testing
Testing involving customer data
Regulatory Compliance: Verify testing approach complies with all applicable regulations in your jurisdiction and industry.
Incident Planning: Develop legal response plans for various scenarios (discovered active breaches, testing-related system failures, data exposure).
Many organizations find that engaging professional penetration testing firms with established legal frameworks (like Cyberlords) reduces legal counsel costs, as standardized agreements and processes require minimal customization.
Understanding and meeting legal requirements for hiring hackers isn’t just about compliance—it’s about enabling effective security testing. Proper authorization, comprehensive contracts, data protection compliance, and responsible disclosure create the framework for successful ethical hacking engagements that strengthen security without legal risk.
The complexity of legal requirements underscores the value of working with established security firms that handle these requirements as part of their standard process. When you work with Cyberlords, our team manages all legal documentation, compliance requirements, and industry-specific regulations, allowing you to focus on improving security rather than navigating legal complexity.
Ready to engage in legally compliant penetration testing? Contact Cyberlords today for a free consultation. Our certified ethical hackers provide comprehensive security testing with complete legal compliance, professional liability insurance, and industry-leading contracts and NDAs. Request your complimentary security assessment consultation now.
Q1: Is it legal to hire a hacker for penetration testing without involving legal counsel?
Yes, it is legal to hire ethical hackers for penetration testing without legal counsel, provided you obtain proper written authorization and use a comprehensive penetration testing agreement covering all essential legal protections (scope, confidentiality, liability, data handling). However, for large organizations, critical systems, or complex regulatory environments (healthcare, finance, government), legal counsel review is highly recommended to ensure complete compliance. Working with established firms like Cyberlords who provide standardized, legally sound agreements can reduce or eliminate the need for extensive legal counsel involvement, as their contracts already address standard legal requirements and have been reviewed by legal experts.
Q2: What happens if penetration testing accidentally causes system damage or downtime?
Well-drafted penetration testing agreements should address accidental damage through liability and insurance provisions. Typically, the ethical hacker’s professional liability (E&O) insurance covers unintended damages from testing activities, within defined limits. The agreement should specify liability caps, insurance coverage amounts, and procedures for reporting and addressing incidents. Organizations should also ensure the ethical hacker carries adequate insurance (minimum $1-2 million coverage for significant engagements). Reputable firms like Cyberlords maintain substantial professional liability insurance and use careful testing methodologies to minimize system impact. Prevention is key: thorough planning, staging environments for risky tests, and testing backup/recovery procedures before starting reduce damage risks significantly.
Q3: Do I need separate authorization for each department or system, or can one company-wide authorization cover everything?
Authorization scope depends on your organization’s structure and the systems being tested. A single comprehensive authorization signed by someone with authority over all systems in scope (typically a C-level executive or owner) can cover company-wide testing, as long as the authorization document clearly lists all systems, departments, and infrastructure components included. However, for large organizations, practical considerations may favor department-specific authorizations: IT departments may need to authorize their infrastructure separately, specific business units may control their own systems, or certain systems may be managed by third parties requiring separate permissions. When testing third-party systems or cloud providers, you always need explicit authorization from those parties regardless of your internal authorization. The key is ensuring every system tested is explicitly authorized by someone with legal authority over that system.
legal requirements hiring hackers guide overview
Key decisions, risks, and implementation actions for legal requirements hiring hackers guide.
These platforms offer the broadest talent pools with varying skill levels and competitive pricing:
Upwork
As one of the largest freelancing platforms globally, Upwork hosts thousands of cybersecurity professionals offering ethical hacking, penetration testing, and security consulting services.
Pricing: Highly variable; $25-150+/hour depending on experience and location.
Fiverr
Fiverr offers a gig-based model where ethical hackers list specific services as “gigs” with set prices. It provides a quick, affordable way to hire for smaller projects.
Strengths:
Fixed pricing for defined services
Fast hiring process
Satisfaction guarantee
Seller levels (New, Level 1, Level 2, Top Rated)
Global talent pool
Best For: Small businesses or projects with limited budgets; well-defined, smaller-scope security tasks (not comprehensive penetration testing).
Considerations: Quality varies significantly; better suited for specific tasks than comprehensive security assessments; always verify credentials and expertise.
Pricing: Lower than other platforms; gigs start at $5 but $100-500+ for substantial security work.
Freelancer
Freelancer.com operates on a bidding model where businesses post projects and receive competitive bids from ethical hackers worldwide.
Self-Managed: Freelance platforms (requires own contracts/NDAs)
Best Practices Regardless of Platform
Whatever platform you choose, follow these best practices:
1. Always Verify Credentials: Even on pre-vetted platforms, independently verify certifications through official channels. Use our credential verification guide for step-by-step instructions.
2. Check References: Request and contact references from previous clients. Ask about work quality, communication, reliability, and results achieved.
3. Start Small: Begin with a limited-scope project to evaluate the ethical hacker’s skills, communication, and professionalism before committing to larger engagements.
4. Define Clear Scope: Create detailed project scope documents outlining exactly what will be tested, methodologies allowed, deliverables expected, and timeline. Ambiguity leads to disappointing results.
5. Establish Legal Protection: Ensure proper contracts, NDAs, and rules of engagement are in place before testing begins. Cyberlords handles this automatically; freelance platforms require you to create these documents.
6. Communicate Expectations: Clearly communicate your security goals, compliance requirements, and reporting needs upfront. Quality ethical hackers will ask detailed questions to understand your environment.
7. Review Sample Reports: Request redacted sample reports from previous engagements to evaluate reporting quality and depth. Poor reporting wastes the value of good testing.
Be cautious of these warning signs on any platform:
Inability or unwillingness to verify certifications
Refusal to provide references or sample reports
Guaranteed results or promises to “hack anything”
Extremely low pricing that seems too good to be true
Poor English communication (for English-language projects)
Pressure to start immediately without proper contracts
Resistance to signing NDAs or legal agreements
Lack of methodology description or testing approach
When you see these red flags, move to the next candidate. The cost of hiring unqualified or unethical professionals far exceeds any savings from low prices.
Conclusion: Making Your Platform Choice
Choosing the best platform to hire ethical hackers depends on your specific needs, budget, and timeline. For most organizations seeking professional, reliable ethical hacking services with verified credentials and comprehensive support, Cyberlords.io offers the ideal solution. You get certified expertise, transparent pricing, legal compliance, and proven results without the risks of unvetted freelancers or the complexity of managing platform-based crowdsourced testing.
For organizations with different needs—such as continuous crowd-sourced testing (HackerOne, Bugcrowd), elite pre-vetted talent on demand (Toptal), or budget-friendly project-based work (Upwork, Fiverr)—the platforms outlined in this guide provide quality alternatives.
Remember that platform choice is just one factor. Proper vetting, clear communication, legal protection, and realistic expectations determine success regardless of which platform you choose.
Ready to hire certified ethical hackers? Visit Cyberlords.io today to request a free consultation with our certified security experts. Discuss your security testing needs, receive transparent pricing, and begin working with verified CEH and OSCP-certified professionals who deliver the high-quality penetration testing your business deserves.
Regional Services: Find Ethical Hackers in Your Country
Looking for ethical hackers in a specific region? Here’s what to consider for local hiring:
🇺🇸 Hire Ethical Hackers in the USA
US-based platforms like Cyberlords, Cobalt, and Synack specialize in CFAA-compliant testing. Look for firms familiar with HIPAA (healthcare), SOX (finance), and state laws like CCPA (California). Most major platforms serve all 50 states with same-day response.
🇬🇧 Hire Ethical Hackers in the UK
UK testers must understand GDPR, the Computer Misuse Act 1990, and FCA cybersecurity requirements. Platforms like Cyberlords, NCC Group, and Context Information Security specialize in UK compliance.
🇨🇦 Hire Ethical Hackers in Canada
Canadian regulations include PIPEDA and provincial privacy laws (PIPA, PHIPA). Ensure your chosen platform understands OSFI guidelines for financial institutions.
🇦🇺 Hire Ethical Hackers in Australia
Australian testers should be familiar with the Privacy Act, APRA CPS 234, and Essential Eight controls. Look for platforms offering AEST timezone support.
🇪🇺 Hire Ethical Hackers in Europe
GDPR compliance is mandatory across all EU member states. The NIS2 Directive adds requirements for critical infrastructure. Platforms with European presence understand country-specific variations.
🌐 Global Coverage
For multinational organizations or other regions, choose platforms like Cyberlords that offer global coverage with local compliance expertise. Contact us for region-specific requirements.
Frequently Asked Questions
Q1: What’s the difference between specialized cybersecurity platforms and general freelance websites for hiring ethical hackers?
Specialized cybersecurity platforms (like Cyberlords, Cobalt, Synack) focus exclusively on security professionals and typically pre-vet all ethical hackers, manage legal agreements, provide quality oversight, and offer compliance-ready reporting. General freelance websites (like Upwork, Fiverr, Freelancer) offer broader talent pools with varying skill levels, require you to vet candidates yourself, and handle your own legal agreements and compliance requirements. Specialized platforms offer higher average quality and less management overhead but typically cost more. Freelance platforms offer lower prices and more flexibility but require significantly more due diligence and risk management.
Q2: Can I trust ethical hackers found on freelance platforms like Upwork or Fiverr?
Yes, but with proper vetting. Many legitimate, certified ethical hackers use freelance platforms to find clients. However, these platforms don’t deeply vet security skills or verify certifications, so you must do this yourself. Always independently verify certifications through official channels (EC-Council for CEH, OffSec for OSCP, etc.), check references thoroughly, review portfolios and past work, conduct technical interviews, and start with small test projects. Use our detailed credential verification guide to ensure candidates hold the certifications they claim. Never hire based solely on platform profiles or reviews—always perform independent validation.
Q3: How much should I expect to pay for ethical hacking services across different platforms?
Pricing varies significantly by platform and expertise level. Premium specialized platforms (Cyberlords, Toptal, Synack) typically range from $5,000-$50,000+ for comprehensive penetration testing, with hourly rates of $150-250+ for consulting. Mid-tier platforms (Arc.Dev, Cobalt) run $75-150/hour. General freelance platforms offer the widest range: qualified professionals on Upwork charge $50-150/hour, while Fiverr gigs for substantial security work run $100-500+. Be skeptical of extremely low prices—comprehensive penetration testing requires significant time, expertise, and specialized tools. The cheapest option often leads to inadequate testing or hidden costs. For detailed cost breakdowns, see our guide on the cost to hire a hacker.
It starts with a click. Or sometimes, no click at all.
Your battery drains a little faster. Your phone feels warm in your pocket. You hear a faint echo on calls. These aren’t just “bugs”—they are often signs of commercial-grade spyware.
For high-net-worth individuals, executives, and public figures, the threat isn’t just a “virus.” It’s targeted surveillance tools like Pegasus, Predator, or commercial stalkerware used by competitors or hostile parties.
At Cyberlord, we specialize in Mobile Forensics. This guide isn’t for the average user; it is for those who have real assets to protect. Here is how we detect, remove, and prevent iPhone compromise.
🚨 Section 1: Is Your iPhone Infected? (The Symptoms)
Hackers don’t want you to know they are there. But they leave footprints.
1. The Heat Signature
Malware runs in the background, constantly uploading your data to a Command & Control (C2) server. This CPU usage generates heat. If your iPhone 15 Pro gets hot while sitting on your desk, be alarmed.
2. The “Ghost” Data Usage
Go to Settings > Cellular. Scroll down. Do you see “System Services” utilizing gigabytes of data? Or an app like “Calculator” using data? Spyware disguises itself as system processes to exfiltrate your photos and chats.
3. The Configuration Profile Trap
This is the #1 way hackers bypass Apple’s security.
Check: Go to Settings > General > VPN & Device Management.
Action: If you see a “Profile” you didn’t install (often customized to look like a workplace app), DELETE IT IMMEDIATELY. This profile gives them “God Mode” over your device.
🛡️ Section 2: The “Cyberlord Forensic Wash” (Our Service)
Standard antivirus apps cannot find Pegasus. It lives in the kernel memory.
If you believe you are targeted, simple resets aren’t enough. You need a Forensic Wash.
What Our VIP Service Does:
Sysdiagnose Analysis: We extract the hidden 200MB log files from your iOS kernel.
Network Traffic Inspection: We analyze your outbound packets to identify connections to known C2 spyware servers.
Sterilization: Our certified forensic examiners guide you through a “DFU Mode” hardened reset that wipes the firmware itself, ensuring even persistent threats are nuked.
Don’t risk your reputation or millions in assets.Get a confirmed “Clean Bill of Health” for your device today.
📱 Book a VIP iPhone Security Audit
suspect you are bugged? Let our forensic team analyze your device logs remotely and secure your digital life.Schedule Forensic Analysis ($1,000)
🔒 Section 3: Professional Protection Tools (DIY)
If you aren’t ready for a full audit, you must install these essential barriers immediately.
1. Encrypt Your Traffic (VPN)
Hackers often intercept data at the network level (Public Wi-Fi, Hotels).
Solution:NordVPN (Rated #1 for iOS). It wraps your traffic in military-grade encryption so hackers see nothing but noise.
Features: Threat Protection Lite (blocks malicious ads/links).
If you are a journalist, politician, or under active attack, Apple built a secret weapon for you.
Enable Lockdown Mode:
Go to Settings > Privacy & Security.
Scroll to bottom > Lockdown Mode.
Turn it ON.
What it does:
Blocks most message attachments (where exploits hide).
Blocks incoming FaceTime calls from strangers.
Disables complex web browsing features.
Effect: It makes your phone “boring” but nearly invincible to commercial spyware.
Conclusion: Paranoia is Good protection
In 2025, your phone is the key to your bank, your business, and your secrets. Hackers know this.
You have two choices:
Hope Apple’s default security is enough.
Verify.
If you notice odd behavior, do not ignore it. Install a VPN, run a Clario scan, and if the symptoms persist—contact Cyberlord for a professional forensic extraction.
A: Yes. These are called “Zero-Click” or “One-Click” exploits. Advanced spyware like Pegasus can infect your device just by receiving a specific iMessage, without you even opening it. This is why Lockdown Mode and professional analysis are vital for high-risk targets.
Q: Does a Factory Reset remove hackers?
A: Usually, yes. However, advanced “persistence” malware can survive a standard reset. To be 100% sure, you must perform a DFU (Device Firmware Update) Restore using a computer, which wipes and rewrites the core operating system.
Q: Can Cyberlord remove Pegasus remotely?
A: We can detect the specific “Indicators of Compromise” (IOCs) using generated logs you send us. If detected, we guide you through the military-grade sanitization process to ensure the threat is eradicated.
how to protect iphone from hackers guide overview
Key decisions, risks, and implementation actions for how to protect iphone from hackers guide.
If you need to know how to receive text messages from another phone number, begin with one question: do you own or have clear authority to manage that number and device? If the answer is yes, you may be able to use Apple or Google synchronization, a carrier service, a family-safety app, or business device management. If the answer is no, do not attempt to access the messages.
This guide compares free synchronization, paid monitoring tools, compatibility checks, privacy questions, and the warning signs behind services that promise private messages from only a phone number.
Authorized-use notice: Use these methods only for a number you own, a minor child’s device you are legally permitted to supervise, or an organization-owned device covered by clear written policy and notice. This article is general information, not legal advice.
Start with the lawful option that matches your situation
The right method depends on ownership, operating system, and purpose. For your own number, official synchronization is usually the simplest and least expensive answer. For a child’s device, a paid family-safety product may add a dashboard and alerts, but only when parental monitoring is lawful and proportionate. For a company phone, mobile device management and written policy are generally more appropriate than a consumer monitoring app.
Situation
Best starting point
What you need
Your number on a second Apple device
Messages in iCloud or Text Message Forwarding
The same Apple Account and trusted-device access
Your Android messages on a computer or tablet
Google Messages device pairing
The phone, Google account, and an internet connection
A minor child’s device
Transparent family rules plus a compatible parental tool
Legal authority, setup access, and a defined safety purpose
A company-owned phone
Mobile device management
Ownership records, employee notice, policy, and limited admin access
Another adult’s private phone
None without valid consent or legal authority
Ask for permission; do not buy covert-access services
US federal law generally prohibits intentional interception of electronic communications unless an exception applies. Consent and workplace-monitoring rules can also vary by state. Device ownership alone is not automatic permission to read every conversation. Seek qualified local legal advice when authority is disputed, an adult partner is involved, or monitoring could affect employment.
Use Apple or Google sync for a number you own
Official tools are the best first choice when you simply want your own texts on another screen. Apple explains that Text Message Forwarding can make SMS, MMS, RCS, and iMessage conversations available on supported Apple devices signed in to the same Apple Account. Messages in iCloud can keep message history updated across trusted devices. Availability may still depend on device, carrier, region, and current software.
For Android, Google Messages for web pairs the Messages app with a computer or Android tablet. The phone needs an internet connection. Unpair shared or old computers because cached conversations can expose verification codes and personal information.
Before buying anything, remove account sessions you do not recognize, enable two-factor authentication, and secure the carrier account against unauthorized SIM changes. If a phone is lost, use the official recovery and replacement process. A monitoring product will not repair a compromised Apple, Google, or carrier account.
Official sync is not the same as secretly cloning a number. It relies on authenticated accounts, trusted devices, or pairing. Any website claiming it can display anyone’s messages from a phone number alone, with no account verification or device access, is not offering a credible substitute.
Compare mSpy, Eyezy, and Sphnix before paying
mSpy, Eyezy, and Sphnix are commercial options for authorized family monitoring. Features can change after iOS or Android updates, and visibility differs among SMS, iMessage, RCS, and chat apps. Cyberlord has not independently verified every current feature or device combination. Check current compatibility, setup, privacy, billing, and refund terms before purchase.
Product
Why an authorized buyer may consider it
Verify before checkout
mSpy
A consolidated monitoring dashboard for a compatible, authorized device
Exact OS support, required device access, available message sources, renewal price, cancellation, and refunds
Eyezy
A family-safety product to compare when supervision and alerts are the main goal
Which alerts and message categories work on the specific device, setup steps, data handling, and subscription terms
Sphnix
An additional option for buyers who want to inspect its presented dashboard or demo
Whether the demo reflects current functionality, installation requirements, support access, billing, and refund policy
Take the phone model and operating-system version to the vendor’s compatibility page. Confirm whether physical access, account credentials, installation, or a backup is required. Ask support to answer unclear points in writing and save the checkout terms.
Affiliate disclosure: Cyberlord may earn a commission if you purchase through the sponsored links below, at no additional cost to you. Placement does not mean a product is suitable for every device or legal situation.
Decide whether paid monitoring is actually necessary
A paid app makes sense only when official synchronization does not meet a legitimate supervision need. A parent may want one place to review safety alerts, or a household may need cross-platform support. Those benefits do not remove setup restrictions or legal responsibilities.
Define the problem before choosing a plan: bullying, scam contacts, unsafe links, or a documented welfare concern. Decide what information is necessary and who may review it. Explain age-appropriate rules, restrict dashboard access, and reassess as the child matures. Targeted supervision creates less privacy risk than indefinite collection.
For business phones, document what the company collects, why, who reviews it, and how long it is retained. Mobile device management better fits provisioning, inventory, security settings, remote wipe, and compliance reporting. Consumer parental tools are not a shortcut around HR review or employee notice.
Check compatibility, billing, privacy, and support
Buyers often focus on whether an app says it can show texts. A better decision uses a complete checklist:
Authority: Record why you may manage the device and whether notice or consent is required.
Compatibility: Verify the exact phone model, operating-system version, account type, and message service.
Setup: Confirm whether you need the unlocked phone, account access, a cable, cloud backups, or ongoing physical access.
Coverage: Separate SMS, MMS, RCS, iMessage, and third-party apps instead of assuming “messages” means all of them.
Security: Read how the provider protects dashboard access and stored data. Use a unique password and multifactor authentication when offered.
Billing: Check the initial charge, renewal period, renewal price, taxes, cancellation method, and refund eligibility.
Support: Look for documented support channels and ask a compatibility question before buying.
Removal: Know how to stop collection, uninstall the product, revoke permissions, and delete the account and retained data.
The FTC’s endorsement guidance says financial relationships should be disclosed clearly and conspicuously near recommendations. That is why the commission notice appears beside the purchase links, rather than being buried at the bottom of the page.
Avoid free-access scams and secure your own messages
People searching for how to receive text messages from another phone number free may find pages requesting an Apple Account password, Google recovery code, SIM details, or payment card “for verification.” Do not provide them. Legitimate free methods use services you control, such as Apple sync, Google pairing, carrier features, or verified backups.
Warning signs include guaranteed access to any phone, no setup or authorization requirement, pressure to pay with cryptocurrency, requests to disable device security, and refusal to provide written billing or privacy terms. A polished dashboard preview does not prove that the service can deliver what it advertises.
If you think someone else is receiving your messages, change the Apple or Google password from a trusted device, review account sessions, unpair unknown computers, update the operating system, contact the carrier about SIM and port-out protection, and preserve evidence of suspicious alerts. Our guide on how to tell if your phone has been hacked covers additional defensive checks.
Conclusion
The safest answer to how to receive text messages from another phone number starts with authorization. Use Apple or Google synchronization for your own number. Consider a paid family-safety product only for a compatible device you are lawfully allowed to supervise. Use written policy and business device management for company phones. Never pay for covert access to another adult’s private messages.
When comparing mSpy, Eyezy, and Sphnix, verify the current device support, setup method, message coverage, data practices, renewal price, cancellation process, and refund terms. A careful compatibility check before checkout is more valuable than any broad promise on a sales page.
Frequently asked questions
Can I receive text messages from another phone without having that phone?
Usually not through a legitimate setup. Official synchronization and authorized monitoring tools normally require access to the account, the original device, or prior enrollment. A service promising messages from only a phone number should be treated as a serious warning sign.
Can two phones receive text messages from the same number?
Sometimes. Apple can display messages on trusted Apple devices through Messages in iCloud or Text Message Forwarding, while Google Messages can pair an Android phone with a computer or tablet. Carrier support and regional availability can differ.
What is the best app for receiving a child’s text messages with permission?
There is no universal best app. Compare mSpy, Eyezy, and Sphnix against the child’s device, operating system, message types, setup requirements, price, cancellation terms, and your local law. Verify every feature on the provider’s current website before paying.
If you have ever paid for a “security assessment” and ended up with a spreadsheet of findings you cannot prioritize, you already understand the problem.
The confusion around vulnerability assessment vs penetration testing is one of the most expensive mistakes businesses make in security. One approach gives you breadth and repeatability. The other proves what an attacker can actually do.
This guide shows you exactly what each one is, what you receive at the end, and how to choose the right option based on risk, compliance, and budget.
Quick answer:
Run a vulnerability assessment to find and track exposures across all assets.
Run a penetration test to validate exploitability and measure real impact.
Combine both into a program that includes remediation and retesting.
A vulnerability assessment is a structured process to identify and prioritize known weaknesses across your environment. The emphasis is coverage:
missing patches (CVEs)
weak configurations
exposed services and risky defaults
insecure versions of software and libraries
A good assessment also reduces noise by validating findings, grouping root causes, and producing an actionable remediation plan.
Penetration testing
Penetration testing is a simulated attack performed with written permission. The emphasis is proof:
can a weakness be exploited?
what is the blast radius?
what is the business impact?
Pen tests often include manual testing and deeper logic checks (authentication, authorization, and application workflows) that scanners miss.
2. The biggest differences (table + plain-English explanation)
Breadth vs depth
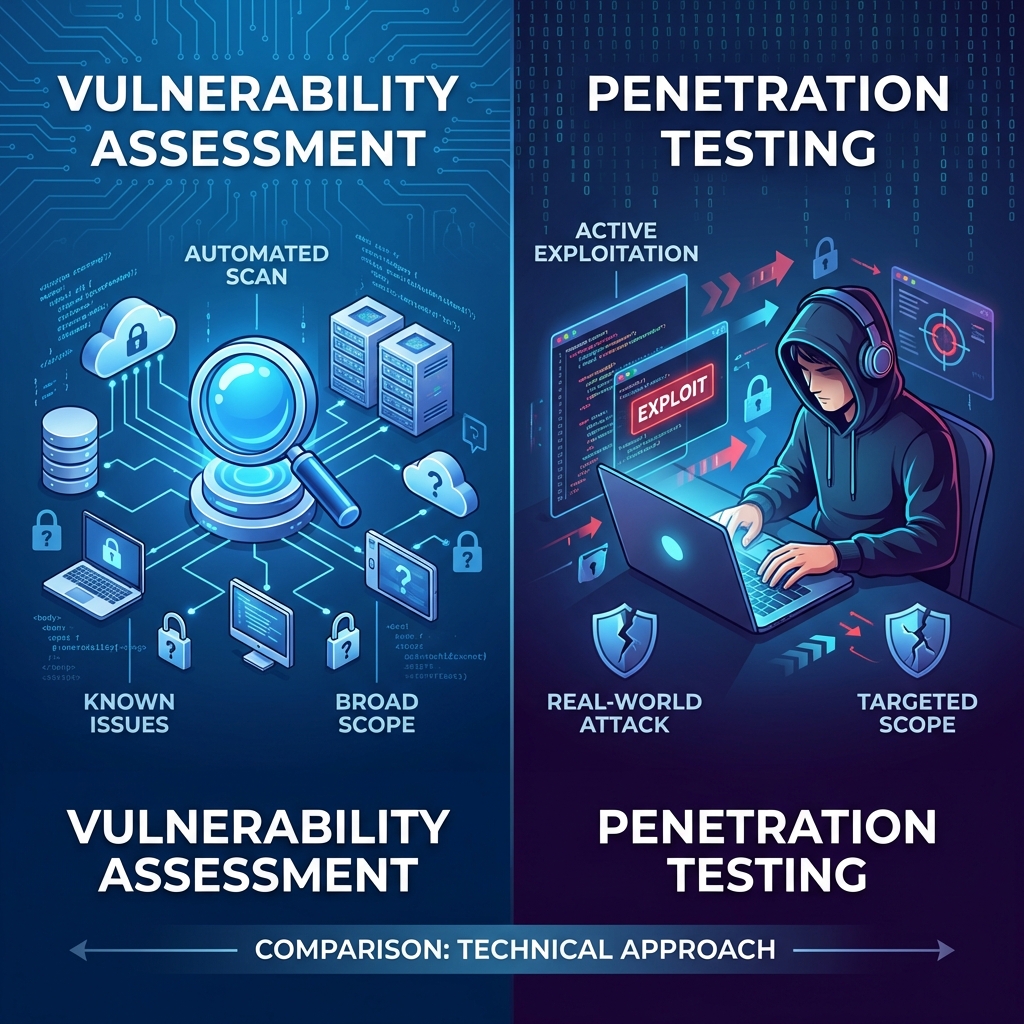
A vulnerability assessment is designed for coverage across many assets. Penetration testing is designed for depth against the paths that matter most.
List vs proof
Assessments help you prioritize what to fix. Pen tests help you prove what is exploitable and what the impact looks like if an attacker chains weaknesses together.
Here is the shortest comparison that still stays accurate:
Area
Vulnerability Assessment
Penetration Testing
Goal
Find and prioritize weaknesses
Prove exploitability and impact
Method
Broad scanning + validation
Manual testing + controlled exploitation
Output
Risk-ranked exposure list
Attack narrative + evidence + fixes
Coverage
Wide (many assets)
Deep (critical assets and paths)
Best for
Continuous hygiene
Go-live validation and assurance
Plain-English analogy:
A vulnerability assessment is an inspection that lists weak doors and windows.
A penetration test is hiring a professional (authorized) to show which doors actually open and what they can access once inside.
3. What you should receive at the end (deliverables)
Vulnerability assessment deliverables
Do not accept “raw scanner output” as the final product.
A strong assessment deliverable includes:
validated findings (reduced false positives)
asset context (what is internet-facing, what is critical)
CVSS plus business risk notes
patch and configuration guidance
a remediation backlog your IT team can execute
If you want a fast way to separate credible vendors from low-quality ones, ask for a redacted sample report.
Penetration test deliverables
A penetration test should include:
executive summary with business risk
technical detail with reproducible evidence
screenshots and proof-of-access where appropriate
attack chains (how small issues combine into major impact)
prioritized remediation and retest options
Pen testing is also where many teams discover identity and access issues, such as overly-permissive roles and weak MFA policies.
4. Cost, time, and operational impact
Typical cost ranges
Prices vary widely by scope, but as a rough reference:
vulnerability assessments are generally lower-cost and repeatable
penetration tests cost more because they require expert time and careful manual work
If you are trying to decide between spending more on testing or fixing what you already know is broken, consider a staged approach: assess, remediate the top risks, then validate with a pen test.
Impact and safety
Assessments are usually low-risk because they are non-intrusive.
Pen tests can be more disruptive if they include aggressive testing. That is why scoping and rules of engagement matter:
test windows
rate limits
explicit exclusions
escalation contacts
If you are new to this, read is hiring a hacker legal so the paperwork and authorization are handled correctly.
5. Compliance and audit expectations
Compliance is not the reason to do security testing, but it often sets a minimum standard.
PCI DSS
PCI environments commonly require routine vulnerability scanning and periodic penetration testing (and retesting after major changes).
SOC 2
Most SOC 2 audits expect evidence of a vulnerability management program and regular testing. A penetration test report is often the simplest artifact auditors understand.
ISO 27001
ISO programs are built around risk management and continuous improvement. Assessments help show ongoing hygiene, while pen tests demonstrate independent validation.
HIPAA and GDPR
Healthcare and privacy-driven environments often use both: assessments for continuous controls and pen tests to validate access boundaries around sensitive data.
6. Building a testing program that actually reduces risk (including Sphnix)
A common failure mode is paying for testing and never closing the loop.
A simple quarterly pattern
Here is a model that works for many businesses:
monthly or continuous vulnerability assessment cadence
remediation sprint focused on critical and high-risk items
penetration test after major releases or at least annually
retest to confirm fixes
If you want a program that also measures detection and response (not just exposures), add a red team layer. See red team vs blue team vs purple team.
Sphnix Monitoring App: where it can fit (lawful use only)
Testing tells you what is wrong. Monitoring helps you see what is happening after changes are made.
If you need visibility into company-owned mobile devices (or parental monitoring for minors, with appropriate consent and local legal compliance), the Sphnix Monitoring App is marketed as a managed monitoring option.
Frequently mentioned features include:
call and messaging activity visibility
app activity across common messengers
location history and movement patterns
web activity and device usage insights
For a deeper feature breakdown and legal guidance, read our Sphnix review.
Want a recommendation based on your situation? Reach us via contact.
7. Conclusion: choose based on risk, then validate
If you only remember one line, make it this: vulnerability assessments help you manage exposure at scale, while penetration tests prove impact.
Most teams do best when they treat vulnerability assessment vs penetration testing as a sequence, not a debate:
find and prioritize
fix the top risks
validate exploitability
retest and repeat
Next steps
If you want a scoped assessment with clear deliverables, request a proposal here: contact.
FAQs
1. Is a vulnerability scan the same as a vulnerability assessment?
No. Scanning is an automated step. An assessment includes validation, prioritization, and a remediation plan.
2. How long does a penetration test take?
For many small to mid-size scopes, 1-2 weeks is common. Complex environments or multiple apps can take longer.
3. Which one should we do first?
If you have never done either, start with a vulnerability assessment to establish baseline hygiene, then run a penetration test to validate critical paths.
4. Can we do a vulnerability assessment in-house?
Often yes, if you have the tools and expertise. Many teams scan internally and use an external partner for penetration testing to get deeper expertise and independent validation.
5. What should we ask for before signing with a testing vendor?
Ask for written scope, authorization language, a redacted sample report, retest options, and clear expectations on what evidence you will receive.
vulnerability assessment vs penetration testing 2025 guide overview
Key decisions, risks, and implementation actions for vulnerability assessment vs penetration testing 2025 guide.
Every day, I receive dozens of messages asking the same question: “Can you help me hack my partner’s Instagram account?”
The desperation is real. Suspicious activity. Deleted messages. Changed passwords. The urge to know what’s happening on someone’s Instagram, Facebook, or WhatsApp account can feel overwhelming.
If you searched how to hack Instagram accountbecause your own profile is locked or hijacked, start with recovery and evidence preservation instead of trying password tools or Telegram “hackers.” That path is safer, legal, and much more likely to protect your account.
But here’s the hard truth: Hiring a hacker for Instagram, Facebook, or WhatsApp is a federal crime. It violates the Computer Fraud and Abuse Act, carries penalties of up to 10 years in prison, and fines exceeding $250,000. Even attempting to hire someone for this purpose can be prosecuted as conspiracy.
In my decade of cybersecurity work, I’ve seen countless people lose money to scammers, face criminal charges, or destroy relationships by trying to hire a hacker for Instagram or other social media platforms. The consequences are always worse than the problem they were trying to solve.
In this guide, I’ll explain why people search for social media hackers, why it’s a catastrophically bad idea, and—most importantly—what legal, ethical alternatives actually work when you have legitimate security or monitoring concerns.
Why Do People Try to Hire a Hacker for Instagram/Facebook/WhatsApp?
Before we discuss solutions, let’s understand the motivations. People searching to hire a hacker for Instagram, Facebook, or WhatsApp typically fall into these categories:
1. Relationship Suspicions (70% of Requests)
The most common reason. Someone suspects their partner of infidelity and wants to:
Read private Instagram DMs
View deleted Facebook messages
Monitor WhatsApp conversations
See who they’re following or messaging
2. Parental Concerns
Parents worried about their children’s online safety want to:
Monitor who their child is talking to
Detect cyberbullying or predatory behavior
View private social media activity
Track location through social apps
3. Account Recovery
People locked out of their own accounts after:
Forgetting passwords
Being hacked themselves
Losing access to recovery email/phone
Account suspension or deletion
4. Business Espionage
Competitors or employers wanting to:
Monitor employee social media
Spy on competitor marketing strategies
Access private business communications
5. Revenge or Harassment
Malicious actors seeking to:
Embarrass someone with private content
Steal personal information
Impersonate the victim
Blackmail or extort
The Problem: While some of these concerns are legitimate, hiring a criminal hacker is never the answer.
Why You Should NEVER Hire a Hacker for Instagram/Facebook/WhatsApp
Let me be crystal clear about what happens when you try to hire a hacker for Instagram or other social media platforms:
Legal Consequences Are Severe
Federal Charges: Violates Computer Fraud and Abuse Act (CFAA)
Prison Time: 5-10 years for unauthorized access to electronic communications
Massive Fines: $250,000+ in federal penalties
Civil Lawsuits: The victim can sue you for damages
As we detailed in our legal guide, even attempting to hire someone for this purpose can be prosecuted.
You’ll Get Scammed (99.9% Guaranteed)
The “hackers” advertising Instagram/Facebook/WhatsApp hacking services are almost exclusively scammers:
Common Scams:
The Upfront Payment Scam: Demand $200-$1,000 in Bitcoin, then disappear
The “Verification Fee” Scam: Ask for multiple payments for “verification”
The Malware Scam: Sell you “hacking software” that steals YOUR data
The Blackmail Scam: Take your money, then threaten to report you to police
Real Statistics: Over 95% of people who try to hire social media hackers lose money and get nothing in return.
It Destroys Trust and Relationships
Even if you could successfully hack someone’s account:
You’ve violated their privacy and trust
The relationship is irreparably damaged
You may face restraining orders or harassment charges
The psychological harm is severe
Better Alternative: If you don’t trust your partner, the relationship needs counseling or ending—not illegal surveillance.
The Cyberlord Alternative: Ethical Cybersecurity Experts
If you have legitimate security concerns, don’t hire a criminal hacker. Hire a certified cybersecurity professional like Cyberlord.
What We Do (Legally)
Unlike illegal “hackers for hire,” ethical cybersecurity firms provide legal, transparent services:
Social Media Security Audits: Test YOUR OWN accounts for vulnerabilities
Account Recovery Assistance: Help you regain access to locked accounts through official channels
Corporate Social Media Security: Protect your business accounts from hacking
Employee Monitoring Solutions: Legal monitoring of company-owned devices
Incident Response: If you’ve been hacked, we help you recover legally
The Key Difference: We only work on accounts you legally own or have written authorization to access. We operate within the law, carry professional liability insurance, and provide documented reports.
Why Hackers Use Tracking Apps (And Why You Should Too)
Here’s an uncomfortable truth: malicious actors don’t actually “hack” Instagram or Facebook accounts most of the time. They use legal monitoring apps for illegal purposes.
How Tracking Apps Work
Apps like mSpy and Sphnix are designed for legal parental control and employee monitoring. They can:
Monitor social media activity (Instagram, Facebook, WhatsApp)
Track GPS location
View messages and call logs
Access photos and videos
Record keystrokes
The Legal Way to Use These Apps
These apps are 100% legal when used for:
Parental Control: Monitoring your minor child’s device (that you own)
Read our detailed mSpy review to understand all features and legal requirements.
2. Sphnix – Best for Multi-Platform Families
Sphnix excels at monitoring multiple devices and social platforms:
Cross-platform support (iOS and Android)
All major social media apps
Web filtering and app blocking
Screen time management
Cost: $16.67 – $49.99/month Legal Use: Family safety and parental control
Our Sphnix review covers setup and legal considerations.
Important Legal Disclaimer
Using monitoring apps to spy on a spouse, partner, or anyone without consent is illegal wiretappingand can result in:
Criminal charges
Civil lawsuits
Restraining orders
Divorce proceedings with unfavorable outcomes
The Right Way: If you’re a parent concerned about your child’s social media use, install these apps with transparency and have an honest conversation about online safety.
Why You Need Ethical Hackers (Not Criminal Ones)
When you have legitimate cybersecurity concerns, you need professionals who operate within the law.
What Ethical Hackers at Cyberlord Do
Social Media Security Assessments: Test your business accounts for vulnerabilities
Social Engineering Testing: Identify if your employees are susceptible to phishing attacks via social media
Incident Response: If your account has been compromised, we help you recover it legally
Security Training: Teach your team to recognize and prevent social media attacks
Real-World Example
A client’s Instagram business account (200k followers) was compromised. Instead of hiring an illegal hacker, they contacted Cyberlord. We:
Worked with Instagram’s official support
Identified the security vulnerability (weak password + no 2FA)
Recovered the account within 48 hours
Implemented security measures to prevent future attacks
Cost: $2,500 (vs. $5,000+ scam attempts)
The Difference: Legal, documented, professional service with guaranteed results.
Detecting Social Media Hackers: Use Clario for Protection
If you’re worried that someone might be trying to hack YOUR social media accounts, use professional security tools.
Clario: Comprehensive Social Media Security
Clario is a cybersecurity app designed to detect hacking attempts and protect your accounts:
Key Features:
Data Breach Monitoring: Alerts if your social media credentials appear in leaks
Spyware Detection: Scans for monitoring apps installed without consent
Stalkerware Detection: Identifies “legitimate” apps being used maliciously
24/7 Expert Support: Live chat with cybersecurity professionals
VPN Protection: Secures your connection when using social media on public Wi-Fi
Fraud Link Checker: Identifies phishing attempts targeting your accounts
Cost: $12.99/month for up to 3 devices Platforms: iOS, Android, macOS
How It Protects You:
Detects if someone installed monitoring software on your phone
Alerts you to compromised passwords
Identifies suspicious login attempts
Provides expert guidance on securing accounts
Legal Ways to Recover or Secure Social Media Accounts
If you have legitimate access needs, here are the legal alternatives:
For Account Recovery
Use Official Recovery Tools: Instagram, Facebook, and WhatsApp all have account recovery processes
Contact Support: Reach out to platform support teams
Verify Your Identity: Provide government ID if required
Have an Honest Conversation: Explain why you’re concerned
Use Parental Control Apps: Install mSpy or Sphnix with transparency
Set Clear Boundaries: Establish rules about social media use
Monitor Together: Review activity with your child present
For Business Security
Hire Cyberlord: Professional social media security assessment
Implement Security Policies: Require strong passwords and 2FA
Employee Training: Educate staff on social engineering attacks
Monitor Company Accounts: Legal monitoring of business-owned accounts
Conclusion: Choose Legal Protection Over Criminal Hacking
The urge to hire a hacker for Instagram, Facebook, or WhatsApp is understandable. Social media has become central to our lives, and concerns about safety, fidelity, or security are real.
But the solution is never illegal hacking. The consequences—criminal charges, financial loss, destroyed relationships—far outweigh any potential benefit.
Instead, choose legal alternatives:
For Parental Control: Use mSpy or Sphnix with transparency
For Business Security: Hire Cyberlord for professional assessments
For Personal Protection: Use Clario to detect hacking attempts
For Relationship Issues: Seek counseling, not surveillance
Ready to secure your social media accounts the right way? Contact Cyberlord today for a free consultation on legal social media security solutions. We’ll help you protect what matters without breaking the law.
Frequently Asked Questions (FAQs)
1. Can I hire a hacker to recover my own Instagram account? No, you should never hire a “hacker” for account recovery. Instagram has official account recovery processes that are free and legal. If you’re locked out, use Instagram’s “Forgot Password” feature, verify your identity with a government ID if needed, or contact Instagram Support directly. Hiring someone who claims they can “hack” your account back is almost always a scam, and even if they succeed, they now have access to your account and could steal it permanently or blackmail you.
2. Is it legal to use mSpy on my spouse’s phone? No, it is illegal to install monitoring software on your spouse’s phone without their explicit consent, even if you’re married. This constitutes illegal wiretapping under federal law and can result in criminal charges and civil lawsuits. The only legal uses for monitoring apps are: (1) monitoring your minor child’s device that you own, (2) monitoring company-owned devices with employee notification, or (3) monitoring your own device. For relationship concerns, consider couples therapy or honest communication instead of illegal surveillance.
3. How can I tell if someone installed a monitoring app on my phone? Look for these warning signs: unusual battery drain, increased data usage, phone overheating, unfamiliar apps with generic names, or strange behavior like apps opening randomly. Use a security app like Clario to scan for spyware and stalkerware. Check your installed apps list for anything you don’t recognize. Review app permissions—monitoring apps typically request access to messages, location, camera, and microphone. If you find monitoring software installed without your consent, document it (take screenshots), perform a factory reset, change all your passwords, and consider filing a police report.
hire hacker social media 2025 guide overview
Key decisions, risks, and implementation actions for hire hacker social media 2025 guide.
In the last decade of working in cybersecurity, the most common question I receive isn’t technical—it’s financial: “How much does it cost to hire a hacker?”
Whether you’re a business owner needing to secure your infrastructure or an individual facing a complex digital dilemma, the pricing landscape for ethical hacking services can be opaque and confusing. In 2025, the stakes are higher than ever. With the average cost of a data breach projected to exceed $10 million, investing in security is no longer optional. But that doesn’t mean you should pay blindly. Knowing fair pricing is essential to hire a hacker safely without being overcharged.
The cost to hire a hacker for legitimate services varies wildly—from $50/hour for a freelancer to over $150,000 for a comprehensive enterprise red team engagement. Understanding what drives these costs is the difference between a smart investment and a wasted budget (or worse, falling for a scam).
In this guide, I’ll break down the real costs of ethical hacking services in 2025, exposing the factors that influence pricing and helping you budget for the security you actually need.
The Real Cost of Ethical Hacking Services in 2025
Let’s get straight to the numbers. For professional, legitimate services, you aren’t paying for a “hack”—you are paying for a vulnerability assessment or penetration test.
Here is a breakdown of current market rates for 2025:
Service Type
Typical Cost Range
Ideal For
Basic Vulnerability Scan
$500 – $3,000
Small businesses, compliance checks
Web App Penetration Test
$5,000 – $30,000
SaaS platforms, e-commerce sites
Network Penetration Test
$10,000 – $40,000
Corporate networks, internal systems
Mobile App Security Test
$7,000 – $35,000
iOS and Android applications
Red Team Operation
$50,000 – $150,000+
Large enterprises, mature security programs
This is the biggest cost driver. Testing a simple 5-page marketing website is vastly different from testing a complex healthcare platform with 50 user roles and API integrations.
Number of Assets: How many IP addresses, servers, or applications need testing?
User Roles: Does the app have different permission levels (e.g., Admin, User, Manager) that all need separate testing?
Codebase Size: Larger applications require more time to analyze thoroughly.
2. Testing Methodology (Black, Gray, vs. White Box)
Black Box ($$$): The hacker starts with zero knowledge, simulating a real-world external attack. This is time-consuming and often more expensive.
White Box ($): The hacker is given full access (source code, documentation). This is faster and more thorough for finding bugs but less like a “real” attack simulation.
Gray Box ($$): A balance of both, often the most cost-effective choice for businesses.
3. Tester Expertise and Certifications
You are paying for the brain, not just the tools. A junior tester might charge $100/hour, but a senior engineer with certifications like OSCP (Offensive Security Certified Professional) or CISSP will command $300+ per hour.
Why pay more? An expert can find subtle, critical logic flaws that automated tools and junior testers miss. As we explored in White Hat vs. Black Hat, the expertise of a white hat professional is your best defense against malicious actors.
Hourly Rates vs. Fixed Project Fees
When budgeting, you’ll typically encounter two pricing models.
The Fixed-Fee Model (Project-Based)
Most professional penetration testing firms prefer this. You agree on a scope (e.g., “Test the mobile app”), and they give you a flat price (e.g., “$15,000”).
Pros: Predictable budget, clear deliverables.
Cons: Rigid scope; if you add new features mid-test, it requires a change order.
The Hourly Rate Model
Freelancers and consultants often charge by the hour.
Freelance Rates: $50 – $150 per hour.
Agency Rates: $200 – $500 per hour.
Warning: Be cautious with hourly engagements for open-ended tasks. Without a cap, costs can spiral. Always ask for a “Not To Exceed” (NTE) clause in your contract.
The “Hire a Hacker for Phone” Myth vs. Reality
A significant portion of search traffic for “cost to hire a hacker” comes from individuals wanting to monitor a spouse or partner’s phone.
Let’s be clear: Hiring someone to break into a phone you don’t own is illegal. Legitimate ethical hackers will not perform this service.
However, there are legal alternatives for monitoring devices you own (like your child’s phone) or for employee monitoring on company devices.
Legal Monitoring Software: Apps like mSpy or Eyezy cost significantly less than hiring a professional—typically $10 – $50 per month.
The Cost Difference: A scammer might ask for $500 in Bitcoin to “hack a phone” (and deliver nothing). A legitimate monitoring app costs a fraction of that and actually works.
Read our mSpy review to understand the legitimate costs and features of these tools.
Hidden Costs You Might Not Expect
When budgeting for the cost to hire a hacker, don’t forget these often-overlooked expenses:
1. Retesting Fees
After the hacker finds vulnerabilities, you fix them. But how do you know the fix worked? You need a retest.
Some firms include one round of retesting in the initial price.
Others charge an hourly rate (e.g., $250/hr) for verification.
Tip: Always negotiate one free retest into your contract.
2. After-Hours Testing
If you require testing to happen only on weekends or nights to avoid disrupting business operations, expect a 20-50% premium on the standard rate.
3. Emergency Response
If you are currently under attack and need immediate Incident Response, pricing changes. Emergency rates can easily double standard consulting fees, often starting at $400 – $600 per hour with a substantial retainer upfront.
The cost to hire a hacker varies, but for a legitimate, professional engagement in 2025, you should budget:
$10,000 – $30,000 for a standard business penetration test.
$100 – $300/hour for expert consulting.
$10 – $50/month for legal monitoring software (personal use).
Security is not a commodity; it’s a capability. When you hire an ethical hacker, you aren’t just paying for a report—you’re paying for the peace of mind that comes from knowing your vulnerabilities before the bad guys do.
Ready to secure your assets? Don’t guess at the cost. Contact Cyberlord today for a transparent, custom quote tailored to your specific needs and budget.
Frequently Asked Questions (FAQs)
1. Can I hire a hacker for $50? No, legitimate ethical hackers do not work for $50. Professionals charge hourly rates commensurate with highly specialized IT experts ($100-$300/hr). Offers for “cheap hacking” are almost always scams designed to steal your money or identity.
2. Why is penetration testing so expensive?Penetration testing requires highly specialized skills, expensive tools, and significant time. A thorough test involves manual analysis by a certified expert (OSCP, CISSP) to find complex logic flaws that automated scanners miss. The cost reflects the expertise required to protect your business from potential million-dollar breaches.
3. Do you charge upfront for hacking services?Legitimate firms typically operate on a contract basis. For project-based work, a common structure is 50% upfront and 50% upon delivery of the final report. For hourly consulting, a retainer is often required. Be very wary of anonymous individuals on Telegram or the dark web demanding 100% upfront payment in cryptocurrency.
cost to hire hacker 2025 guide overview
Key decisions, risks, and implementation actions for cost to hire hacker 2025 guide.