Blog

  • Anatomy of the SolarWinds Hack: What Security Teams Should Know

    The SolarWinds hack is one of the most significant cybersecurity breaches in history, exposing critical vulnerabilities across the globe. Understanding its anatomy not only sheds light on advanced hacking techniques but also highlights why investing in ethical hacking tools and pursuing an ethical hacker course is vital for todayโ€™s cybersecurity professionals.

    Table of Contents

    Anatomy of the SolarWinds Hack: What You Must Know
    Anatomy of the SolarWinds Hack: What You Must Know

    In this article, we break down the SolarWinds hack in simple terms, explore its tactics, and show you how resources like SpyWizards can help you strengthen your defenses. If youโ€™re serious about cybersecurity, ethical hacking, and network security penetration testing, read on.


    What Was the SolarWinds Hack?

    In late 2020, cybersecurity experts uncovered a sophisticated cyberattack targeting SolarWinds, a major IT management company. Hackers compromised SolarWindsโ€™ Orion software platform, pushing out updates that contained hidden malwareโ€”a classic supply chain attack.

    This malware, known as SUNBURST, infiltrated thousands of organizations, including Fortune 500 companies and government agencies.

    Learning how hackers execute such attacks is part of any solid ethical hacking tutorial for beginners, especially when preparing for real-world threats.


    How the Attack Unfolded

    The SolarWinds hack involved several key steps:

    1. Initial Breach: Hackers likely gained initial access using stolen credentials or exploiting wireless network vulnerabilities.
    2. Insertion of Malware: Malicious code was stealthily inserted into SolarWindsโ€™ legitimate software updates.
    3. Command and Control (C2): Once the malware was installed, attackers could remotely control the infected systems.
    4. Stealth and Persistence: The malware used techniques to avoid detection for months.

    Understanding the OSI model in network security and TCP/IP basics for hackers is crucial to grasp how attackers moved through networks unnoticed.

    For a deeper dive into these topics, check out our ethical hacking tools guide and ethical hacking tutorials for beginners.


    Techniques Used by Hackers

    The SolarWinds attackers used a wide variety of advanced techniques that any aspiring ethical hacker should study:

    • Credential Theft: Stolen admin credentials allowed privileged access.
    • Lateral Movement: After gaining a foothold, hackers moved through internal networks.
    • Data Exfiltration: Sensitive data was extracted without alerting network defenses.
    • Cloaking Techniques: The malware mimicked normal network traffic to avoid detection.

    Setting up a penetration testing lab setup is a great way to practice and understand how these movements happen in a controlled environment.


    Lessons from the SolarWinds Hack

    The SolarWinds hack teaches valuable lessons:

    1. Never Trust Automatic Updates Blindly

    Even trusted vendors can be compromised. Always verify updates through network security penetration testing.

    2. Segment Your Networks

    Applying concepts from the OSI model in network security helps limit damage when breaches occur.

    3. Invest in Ethical Hacking Skills

    Learning how to become an ethical hacker is no longer optionalโ€”itโ€™s a necessity. With a proper ethical hacker course, you can become the line of defense your organization desperately needs.

    Ready to get started? Explore our ethical hacker courses and become a cybersecurity expert.


    How to Scan Your Network Like a Pro

    One of the most important defensive strategies is proactive scanning. Mastering how to scan a network with Nmap can help you detect vulnerabilities before attackers exploit them.

    Nmap is a powerful, open-source tool that can help you map your network, identify open ports, and find security risks early. We offer an easy ethical hacking tutorial for beginners on using Nmap and other essential tools.


    How SpyWizards Helps You Stay Ahead
    Anatomy of the SolarWinds Hack: What You Must Know

    At SpyWizards, we are dedicated to empowering ethical hackers and cybersecurity enthusiasts with top-tier tools, courses, and tutorials. Whether youโ€™re learning how to become an ethical hacker, exploring penetration testing lab setups, or diving deep into wireless network vulnerabilities, we have you covered.

    Learn, practice, and master cybersecurity โ€” visit SpyWizards today.


    Final Thoughts

    The SolarWinds hack revealed how fragile even the most secure systems can be. Itโ€™s a wake-up call for businesses, governments, and individuals alike to prioritize cybersecurity education and preparedness.

    Are you ready to step into the world of ethical hacking and defend against the next big threat? Dive into SpyWizardsโ€™ ethical hacking tutorials and start your journey today.
  • IDS vs IPS: Which One to Use in 2026?

    IDS vs IPS: Which One to Use?
    IDS vs IPS: Which One to Use?

    In the realm of network security, two acronyms usually stand guard at the gate: IDS and IPS. Intrusion
    Detection Systems (IDS)
    and Intrusion Prevention Systems (IPS) are critical components
    of any defense strategy. But in 2026, with threats evolving towards AI-driven attacks, which one should you choose?

    Table of Contents

    ๐Ÿ”’ Verified Solution: Sphnix

    Looking for the ultimate monitoring tool in 2026? Sphnix offers undetectable remote installation, real-time tracking, and requires no root or jailbreak.


    โžก Get Sphnix Now (Instant Access)

    โœ“ 100% Undetectable   โœ“ No Root Required

    IDS: The Digital Burglar Alarm

    An IDS is a passive monitoring system. It watches network traffic for suspicious activity and sends an alert when it
    finds something. Think of it like a security camera; it records the crime and alerts you, but it doesnโ€™t stop the
    burglar from breaking the window.

    Pros:

    • No impact on network latency (passive).
    • Great for auditing and learning attack patterns.

    Cons:

    • Requires human intervention to stop the attack.
    • Can be overwhelmed by false positives.

    IPS: The Digital Bouncer

    An IPS sits inline with the traffic flow. It doesnโ€™t just watch; it acts. If it sees a malicious packet, it drops it
    immediately, preventing the attack from reaching its target. Itโ€™s the bouncer at the club door.

    Pros:

    • Stops attacks in real-time.
    • Reduces the workload on security teams.

    Cons:

    • Can block legitimate traffic (false positives cause downtime).
    • Adds slight latency to the network.

    Which One Do You Need in 2026?

    The answer is often both, or a hybrid Next-Generation Firewall (NGFW) that combines them. However,
    for specific use cases:

    • Use IDS if you need visibility without risking downtime.
    • Use IPS if you need active protection for critical assets.

    Mobile โ€œIDSโ€: Spy Apps for Device Security

    While traditional IDS/IPS protect networks, what protects your tailored mobile devices? You need a system that
    detects internal threats or unauthorized usage.

    Apps like Sphnix act as a form of โ€œHost-based IDSโ€ (HIDS) for mobile phones. They monitor activity
    logs, messages, and locations to ensure the device isnโ€™t being used maliciously (e.g., by a rogue employee or a
    child in danger).

    Other mobile security monitoring tools include:

    • mSpy: Monitors data flow
      on the device.
    • Eyezy: Uses AI to detect
      patterns, similar to a network Heuristic IDS.

    Conclusion

    Whether you choose IDS or IPS depends on your risk tolerance and infrastructure. But donโ€™t forget the endpoints.
    Securing the network gate is useless if the devices inside are compromised. Use tools like Sphnix,
    mSpy, and Eyezy to extend your security
    visibility to every phone in your organization or family.

    Frequently Asked Questions

    Is Firewal same as IPS?

    No. A firewall blocks traffic based on rules (IP/Port). An IPS inspects the *contents* of the packet to find
    malicious code or exploits.

    Can Sphnix replace an IPS?

    No. Sphnix monitors *user activity* on a phone. An IPS monitors *network packets*. They complement each other.

    What is a false positive?

    When the system flags legitimate traffic as malicious. In an IPS, this means blocking a real user. In an IDS, itโ€™s
    just an annoying alert.

    Do I need hardware for IDS?

    Not necessarily. In 2026, many IDS solutions are software-based or cloud-native (like Snort or Suricata running on
    VMs).

    Is AI used in IDS/IPS?

    Yes, AI is standard in 2026 to detect โ€œzero-dayโ€ attacks that donโ€™t match known signatures.

    Related Spy Wizards Resources

    Safety and Authorization Note

    Use cybersecurity guidance only on accounts, devices, and networks you own or are clearly authorized to review. If you are dealing with account recovery, suspicious logins, device privacy concerns, or business security checks, document what happened, preserve alerts or recovery emails, and avoid sharing passwords, one-time codes, private keys, or financial details. Spy Wizards focuses on lawful support, ethical security review, privacy protection, and practical recovery steps that reduce risk without crossing consent boundaries.

  • Firewall Best Practices for Small Businesses

    Small businesses often buy a firewall and then stop there. That is not enough. A firewall only helps when it is configured, updated, monitored, and matched to the way your business actually works.

    Firewall Best Practices for Small Businesses

    • Change default credentials and lock down admin access.
    • Keep firmware updated.
    • Use least-privilege rules instead of broad allow lists.
    • Review logs and alerts regularly.
    • Separate guest, office, and sensitive systems where possible.

    Most Important Firewall Mistakes to Avoid

    • Leaving remote management open to the internet.
    • Using outdated firmware.
    • Allowing broad inbound access you do not need.
    • Forgetting that cloud apps and remote work change your exposure.

    How Small Businesses Should Think About Firewalls

    A firewall is one part of a security stack, not the whole stack. You still need endpoint security, user training, backups, MFA, and a way to review suspicious events.

    What to Review Quarterly

    • Rule changes.
    • Firmware versions.
    • Admin accounts and MFA.
    • VPN access and remote users.
    • Unexpected traffic patterns.

    For related security work, read network forensics, Nikto for web-server scanning, and Nmap for discovery.

    Request a Small Business Security Review

    Frequently Asked Questions

    Is a firewall enough for a small business?
    No. It is a core control, but it needs to work with MFA, endpoint protection, backups, and access review.

    How often should firewall rules be reviewed?
    Quarterly is a good baseline, and immediately after major system changes.

    Related Security Guides

    Next, read our network-security checklist, our Nessus guide, and our breach-investigation guide.

    Related Spy Wizards Resources

    Safety and Authorization Note

    Use cybersecurity guidance only on accounts, devices, and networks you own or are clearly authorized to review. If you are dealing with account recovery, suspicious logins, device privacy concerns, or business security checks, document what happened, preserve alerts or recovery emails, and avoid sharing passwords, one-time codes, private keys, or financial details. Spy Wizards focuses on lawful support, ethical security review, privacy protection, and practical recovery steps that reduce risk without crossing consent boundaries.

  • How to Secure Your Network as a Professional

    In todayโ€™s digital world, network security is no longer optional โ€” itโ€™s a necessity. Whether youโ€™re a cybersecurity enthusiast, an aspiring ethical hacker, or a seasoned IT professional, mastering how to secure your network as a professional is essential. This guide will walk you through practical steps, essential tools, and key concepts like penetration testing, wireless network vulnerabilities, and ethical hacking techniques.

    Table of Contents

    How to Secure Your Network as a Professional

    How to Secure Your Network as a Professional

    If youโ€™re serious about building your skills, you can also explore our ethical hacker course and discover how to become an ethical hacker with professional guidance.


    1. Understand the OSI Model in Network Security

    Before diving into technical defenses, itโ€™s crucial to understand the OSI model in network security. The OSI (Open Systems Interconnection) model breaks down the complex world of networking into seven layers, each with its own vulnerabilities:

    • Physical Layer: Focuses on hardware protection.
    • Data Link Layer: Deals with MAC address filtering.
    • Network Layer: Where IP addresses and firewalls come into play.
    • Transport Layer: Protects against TCP/UDP-based attacks.
    • Session Layer: Monitors session management.
    • Presentation Layer: Encrypts and decrypts data.
    • Application Layer: Ensures safe end-user communications.

    By securing each layer individually, you build a solid foundation for a resilient network.


    2. Master TCP/IP Basics for Hackers

    Learning TCP/IP basics for hackers is key to understanding how information flows across the internet. TCP/IP protocols are the backbone of data communication. Professionals who grasp packet structures, handshakes, and protocol vulnerabilities can better anticipate and defend against attacks.

    Tip: Practice analyzing packets with tools like Wireshark and gain hands-on experience through a penetration testing lab setup.


    3. Regular Network Security Penetration Testing

    Routine network security penetration testing is a must. Penetration tests simulate real-world attacks, identifying vulnerabilities before malicious hackers do. Effective penetration testing covers:

    • External network assessments
    • Internal network audits
    • Web application security tests
    • Wireless security assessments

    Setting up your own penetration testing lab allows you to practice ethically and legally, boosting your skills in a controlled environment.


    4. Identify and Protect Wireless Network Vulnerabilities

    Wireless networks are often the weakest link in an organizationโ€™s security chain. Professionals must constantly scan for wireless network vulnerabilities like:

    • Weak encryption (e.g., WEP)
    • Default passwords
    • Rogue access points
    • Evil twin attacks

    Upgrade to WPA3 encryption, use strong passphrases, and implement MAC address whitelisting to shield your wireless network effectively.


    5. Ethical Hacking Tools You Need

    Using the right ethical hacking tools can make or break your network security efforts. Popular tools include:

    • Nmap for network scanning
    • Metasploit for vulnerability exploitation
    • Burp Suite for web app security testing
    • Wireshark for network traffic analysis

    Learning how to scan a network with Nmap gives you an edge in discovering potential attack surfaces before hackers do.

    If youโ€™re new to these tools, check out our ethical hacking tutorial for beginners to get started the right way!


    6. Build a Professional Penetration Testing Lab Setup

    Setting up a penetration testing lab setup at home is an excellent way to practice without risking real systems. Essentials include:

    • A dedicated machine running Kali Linux
    • Virtual machines for different operating systems
    • Vulnerable targets like Metasploitable or OWASP Juice Shop
    • Proper network segmentation

    Practice makes perfect, and a home lab allows you to hone your skills safely.


    7. Stay Updated: Continuous Learning is Critical

    How to Secure Your Network as a Professional

    Cybersecurity is an ever-evolving field. New vulnerabilities emerge daily. Stay updated by:

    • Following trusted blogs (like SpyWizards!)
    • Attending cybersecurity webinars
    • Pursuing certifications like CEH, CompTIA Security+, or OSCP
    • Practicing ethical hacking daily

    If youโ€™re serious about your career, consider our ethical hacker course โ€” designed by industry experts to accelerate your journey.


    Final Thoughts: Secure Like a Pro

    Becoming a professional in network security isnโ€™t just about defending systems โ€” itโ€™s about thinking like a hacker to stay one step ahead. Whether youโ€™re learning how to become an ethical hacker or mastering penetration testing, SpyWizards is your ultimate resource.

    Visit SpyWizards today to explore tools, tutorials, and courses that will make you a cybersecurity expert. Your journey to mastering professional network security starts now!

  • Vulnerability Scanning with Nessus: Boost Network Security Like a Pro

    In todayโ€™s digital world, securing your network is more critical than ever. One of the most powerful tools in any ethical hackerโ€™s arsenal is Nessus, a top-tier vulnerability scanner used by cybersecurity professionals worldwide. Whether youโ€™re just diving into an ethical hacker course or youโ€™re a seasoned pro conducting network security penetration testing, understanding how Nessus works is key to staying ahead of cyber threats.

    Vulnerability Scanning with Nessus: Boost Network Security Like a Pro

    Vulnerability Scanning with Nessus: Boost Network Security Like a Pro

    What is Nessus?

    Nessus is a widely used vulnerability scanning tool that identifies and assesses security flaws in operating systems, applications, and network infrastructures. Developed by Tenable, itโ€™s often a central component in penetration testing lab setups. Ethical hackers use Nessus to proactively discover weaknesses before malicious hackers can exploit them.

    Nessus scans a network for vulnerabilities like missing patches, default passwords, misconfigurations, and software bugs. Itโ€™s known for its accuracy, user-friendly interface, and the ability to generate detailed, actionable reports.


    Why Use Nessus for Vulnerability Scanning?

    Nessus helps protect against:

    • Unauthorized access to sensitive data
    • Malware and ransomware infections
    • Data breaches and compliance violations

    Using Nessus for network vulnerability assessments helps you:

    • Improve your understanding of OSI model in network security
    • Get hands-on with TCP/IP basics for hackers
    • Conduct ethical and legal penetration testing

    If youโ€™re exploring how to become an ethical hacker, Nessus is a must-learn tool covered in most ethical hacking tutorials for beginners.


    How Nessus Works: Step-by-Step

    1. Install Nessus: Get started by downloading and installing the software on your local machine or virtual environment.
    2. Configure a Scan: Choose from templates such as โ€œBasic Network Scanโ€ or โ€œAdvanced Scanโ€ depending on your target.
    3. Define Targets: Input the IP addresses or domain names you want to scan.
    4. Run the Scan: Initiate the scan and let Nessus crawl the system for potential security issues.
    5. Review Results: Analyze the report generated, which includes vulnerability severity, potential impact, and remediation tips.
    6. Remediate Vulnerabilities: Apply patches or configuration changes as suggested by Nessus to mitigate the threats.
    7. Re-scan: Validate that vulnerabilities have been resolved and no new issues have appeared.

    Setting Up a Penetration Testing Lab with Nessus

    To get the most from Nessus, integrate it into your penetration testing lab setup. Use virtual machines, routers, firewalls, and vulnerable applications to simulate real-world scenarios. Combine Nessus with tools like Metasploit and Wireshark for comprehensive testing.

    Need help setting up a lab? Check out SpyWizards for expert resources and step-by-step guides.


    Comparing Nessus with Nmap

    Many beginners ask: How does Nessus compare to Nmap? While Nmap is a powerful port scanner and is essential for how to scan a network with Nmap, Nessus goes further by:

    • Checking for known vulnerabilities
    • Scoring risks based on CVSS
    • Offering remediation guidance

    For best results, use both tools together. Scan the network with Nmap first to map devices and ports, then dive deeper with Nessus.


    Wireless Network Vulnerabilities & Nessus

    Nessus can also identify wireless network vulnerabilities, including open ports on wireless routers, default credentials, and outdated firmware. Regular scans help ensure your Wi-Fi networks arenโ€™t easy targets for attackers.


    Get Started with Ethical Hacking Today

    If youโ€™re ready to start your journey or level up in cybersecurity, Nessus is a powerful tool you canโ€™t ignore. Enroll in our comprehensive ethical hacker course, where youโ€™ll master tools like Nessus, Nmap, and Metasploit in real-world simulations.

    Also, explore our full collection of ethical hacking tools and download trusted software directly from our site.


    Final Thoughts

    Vulnerability scanning with Nessus is a foundational skill for anyone interested in ethical hacking or cybersecurity. It offers a proactive approach to securing systems, reducing risk, and maintaining trust in digital operations.

    Visit SpyWizards.com to learn more, download the best hacking tools, and read our latest ethical hacking guides. Want to become an ethical hacker? Youโ€™re in the right place.

  • Netdiscover: Passive Discovery Tool for Ethical Hackers

    Are you curious about how to uncover hidden devices on a network without triggering alarms? Whether youโ€™re a cybersecurity enthusiast, a beginner in ethical hacking, or preparing for a penetration testing lab setup, Netdiscover is a must-have tool in your toolkit.

    Netdiscover: Passive Discovery Tool for Ethical Hackers

    Netdiscover: Passive Discovery Tool for Ethical Hackers

    In this article, weโ€™ll explore how Netdiscover works, its real-world applications in network security penetration testing, and why itโ€™s one of the best ethical hacking tools for identifying wireless network vulnerabilities. If youโ€™re just starting, think of this as an ethical hacking tutorial for beginnersโ€”perfect for building your skills step-by-step.


    ๐Ÿ” What Is Netdiscover?

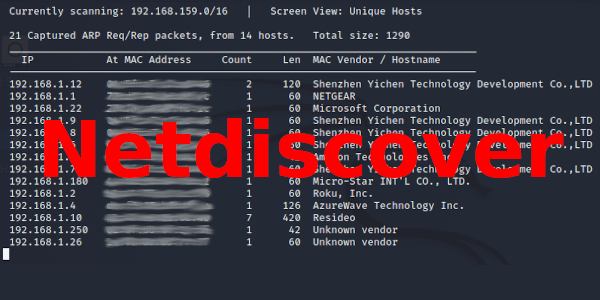
    Netdiscover is a lightweight, passive reconnaissance tool used to discover active hosts on a local network. Unlike active scanners like Nmap, Netdiscover quietly monitors ARP (Address Resolution Protocol) packets to map IP and MAC addressesโ€”making it perfect for stealthy network reconnaissance.

    Whether youโ€™re learning how to become an ethical hacker or setting up your penetration testing lab, Netdiscover helps you understand the basic network structure without raising security flags.


    โœ… Why Ethical Hackers Use Netdiscover

    Netdiscoverโ€™s primary advantage is its passive scanning technique, which is essential for stealth and safety. This makes it ideal for:

    • Mapping internal networks during network security penetration testing
    • Identifying rogue devices or unauthorized hosts
    • Spotting wireless network vulnerabilities in office or home environments
    • Avoiding detection by intrusion detection systems (IDS)

    Learning to use tools like Netdiscover gives you a strong foundation in ethical hacking tools and prepares you for real-world scenarios.


    ๐Ÿ’ก Key Features of Netdiscover

    Hereโ€™s what makes Netdiscover a valuable asset in a hackerโ€™s toolkit:

    • Passive ARP sniffing (stealth scanning)
    • Fast execution and real-time updates
    • Supports both DHCP and static IP environments
    • Works great on Linux-based systems like Kali Linux
    • Requires no complex configuration

    ๐Ÿš€ How to Use Netdiscover: Step-by-Step

    If youโ€™re a beginner, hereโ€™s a simple guide to using Netdiscover:

    1. Open your terminal and run:

    bashCopyEditsudo netdiscover
    

    This command begins scanning the local network for active devices. It will passively monitor ARP requests and display a list of discovered hosts, including IP and MAC addresses.

    2. Scan a specific range:

    bashCopyEditsudo netdiscover -r 192.168.1.0/24
    

    This allows you to target a specific IP range. Perfect when youโ€™re in a large network and want to narrow your results.


    ๐ŸŒ Netdiscover vs Nmap

    While Netdiscover is excellent for passive detection, tools like Nmap are used for active network scanning.

    Check out our full guide on how to scan a network with Nmap for advanced scanning techniques using TCP, UDP, and service detection methods.

    Pro Tip: Use Netdiscover first to map out the network without detection. Then switch to Nmap for deeper analysis.


    ๐Ÿง  Learn the Basics: OSI Model & TCP/IP

    To use tools like Netdiscover and Nmap effectively, itโ€™s important to understand the OSI model in network security and TCP/IP basics for hackers. These concepts help you pinpoint where and how to test for vulnerabilities in any given layer.


    ๐ŸŽ“ Start Your Ethical Hacking Journey

    Whether youโ€™re self-taught or seeking formal training, itโ€™s crucial to follow the right path. Here are some essential resources on how to become an ethical hacker the right way:

    • Take an ethical hacker course to build certified skills
    • Set up a secure and isolated penetration testing lab
    • Practice with real-world tools like Netdiscover, Nmap, Wireshark, and Metasploit

    Explore our detailed ethical hacking tutorial for beginners to get started today.


    ๐Ÿ” Final Thoughts: Why Netdiscover Is a Game-Changer
    If youโ€™re looking for a silent, efficient way to uncover live hosts on a network, Netdiscover is your best friend. Itโ€™s lightweight, effective, and perfect for early-stage network reconnaissanceโ€”an essential phase of penetration testing.

    At SpyWizards.com, we help aspiring cybersecurity experts learn real-world skills with actionable guides and powerful tools. Whether youโ€™re securing your network or learning ethical hacking tools, youโ€™re in the right place.

    Ready to master network discovery? Start with Netdiscover, and let your journey into ethical hacking begin.

  • MAC Address Filtering: Is It Effective?

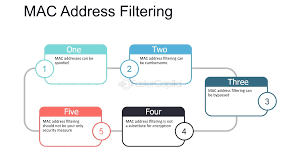
    In the world of network security, MAC address filtering is often promoted as a basic method to control device access. But in todayโ€™s environment, where hackers are becoming more sophisticated, many people are asking: Is MAC address filtering truly effective? In this article, weโ€™ll break down what MAC address filtering is, its strengths, its vulnerabilities, and why it should never be your only line of defense.

    MAC Address Filtering: Is It Effective?

    MAC Address Filtering: Is It Effective?

    If youโ€™re serious about securing your networks, understanding these fundamentals is critical. Letโ€™s dive in!


    What is MAC Address Filtering?

    Every device that connects to a network has a unique identifier known as a MAC address (Media Access Control address). MAC address filtering allows network administrators to specify which devices can access a network based on their MAC addresses.

    When a device tries to connect, the router checks its MAC address against an allowed list. If the address is recognized, the device connects. If not, access is denied.

    At first glance, MAC address filtering seems like a strong gatekeeper for your Wi-Fi โ€” but is it?


    The Effectiveness of MAC Address Filtering

    While MAC address filtering can add a layer of security, it has significant weaknesses:

    1. MAC Addresses Can Be Spoofed

    One of the biggest problems is that MAC addresses can easily be spoofed. With widely available ethical hacking tools like Wireshark and macchanger, an attacker can detect allowed MAC addresses on your network and mimic (spoof) them.

    You can learn more about ethical hacking tools and their uses here.


    2. No Encryption Involved

    Unlike WPA2 or WPA3 protocols that encrypt data transmissions, MAC filtering does not encrypt any data. Itโ€™s simply an access control list. If someone knows your MAC address structure, they can bypass this filter without breaking a sweat.

    For a better understanding of wireless network vulnerabilities, you can check out this detailed guide here.


    3. Management Complexity

    On large networks, maintaining a whitelist of MAC addresses becomes difficult and inefficient. Devices get added, removed, replaced โ€” making constant manual updates a hassle and creating potential gaps in security.

    If youโ€™re setting up a more secure system, learning about penetration testing lab setup is essential. Start your journey with our guide here.


    Why MAC Address Filtering Alone Is Not Enough

    MAC address filtering should be seen as one part of a layered security strategy, not the entire strategy. Smart attackers can monitor network traffic using tools covered in our ethical hacking tutorial for beginners, making it essential to reinforce your defenses.

    Hereโ€™s why MAC filtering needs backup:

    • Lack of Authentication: Anyone spoofing an allowed MAC can instantly connect.
    • Easy Reconnaissance: Wireless traffic, even on secured networks, can leak MAC addresses.
    • False Sense of Security: It may make you complacent, thinking your network is safer than it is.

    Understanding the OSI model in network security can give you a better foundation on how to layer your defenses. Explore it here.


    How Hackers Bypass MAC Address Filtering

    Curious about how hackers get around this defense? Hereโ€™s a simplified explanation:

    1. Scanning Networks: Using tools like Nmap (learn how to scan a network with Nmap here), an attacker identifies connected devices and their MAC addresses.
    2. MAC Spoofing: After identifying a permitted device, the attacker changes their deviceโ€™s MAC address to match.
    3. Access Granted: The spoofed device connects successfully, bypassing MAC filtering entirely.

    If youโ€™re serious about learning more about penetration techniques, consider enrolling in an ethical hacker course.


    Better Alternatives to MAC Address Filtering

    While MAC filtering isnโ€™t entirely useless, it should always be combined with stronger protection methods like:

    • WPA3 Encryption: Always choose the highest encryption available on your router.
    • Network Segmentation: Use VLANs to separate sensitive systems.
    • Strong Password Policies: Ensure Wi-Fi passwords are strong and rotated periodically.
    • Regular Penetration Testing: Conduct network security penetration testing to proactively find and patch vulnerabilities. Learn more here.

    Conclusion: Is MAC Address Filtering Worth It?

    MAC address filtering is helpful but not foolproof. It can slow down casual attackers but wonโ€™t stop a determined one. If you rely solely on MAC filtering for network protection, youโ€™re leaving yourself vulnerable.

    Instead, MAC filtering should be part of a multi-layered security strategy alongside encryption, segmentation, and regular vulnerability assessments.

    Want to dive deeper into cybersecurity? Check out our ethical hacking tutorial for beginners and discover how to become an ethical hacker here!

  • How to Detect and Prevent Rogue Access Points

    In todayโ€™s increasingly connected world, wireless networks are essential for businesses, organizations, and even homes. However, with the convenience of Wi-Fi comes a serious security threat: rogue access points (RAPs). These unauthorized devices can expose your network to dangerous attacks if not properly detected and managed. In this article, weโ€™ll show you how to detect rogue access points and prevent them, using the best techniques and ethical hacking tools to safeguard your network.

    Table of Contents

    How to Detect and Prevent Rogue Access Points

    How to Detect and Prevent Rogue Access Points

    Ready to dive deeper into network security? Visit SpyWizards.com for expert resources and courses on cybersecurity and ethical hacking.


    What is a Rogue Access Point?

    A rogue access point is any Wi-Fi device installed on a secure network without the network administratorโ€™s consent. It could be set up by a well-meaning employee wanting better signal coverageโ€”or by a hacker aiming to steal sensitive data.

    Key dangers of rogue APs include:

    • Data theft
    • Malware injection
    • Network congestion
    • Violation of compliance regulations

    Understanding wireless threats is crucial if youโ€™re serious about securing your systems. Our ethical hacking tutorial for beginners can help you learn the essentials of wireless security.


    How to Detect Rogue Access Points

    1. Wireless Network Scanning

    Perform regular scans using ethical hacking tools like Kismet, AirMagnet WiFi Analyzer, and NetStumbler. These tools identify unknown SSIDs and unusual signals on your network.

    Need help setting up your tools? Check our guide on penetration testing lab setup for a complete walkthrough.

    2. Monitor MAC Addresses

    Authorized network devices have known MAC addresses. By maintaining a whitelist and monitoring for new or unfamiliar MACs, you can quickly spot rogue devices.

    3. Intrusion Detection Systems (IDS)

    Deploy a wireless IDS to detect anomalies in real time. IDS systems can alert you when unauthorized access points are detected, giving you the power to react instantly.

    4. Physical Audits

    Sometimes the simplest solution is the bestโ€”periodically walk through your environment using mobile scanning tools to manually detect rogue hardware.

    Pro Tip: Combine physical audits with a basic understanding of the OSI model in network security for better analysis.


    How to Prevent Rogue Access Points

    1. Establish a Strict Access Policy

    Only authorized personnel should be allowed to install or modify network devices. Implementing a strict device management policy reduces the risk of rogue APs.

    2. Secure Physical Locations

    Ensure your routers, switches, and servers are located in locked rooms or cabinets to prevent unauthorized hardware additions.

    3. Use Strong Encryption

    Always use the strongest encryption methods (WPA3 if possible). Weak or no encryption can make it easier for rogue devices to communicate with your network.

    Want to learn how to become an ethical hacker and master these techniques professionally? Start your journey with us!

    4. Conduct Regular Network Penetration Testing

    Frequent network security penetration testing is crucial for identifying vulnerabilities and rogue devices. By mimicking real-world attacks, you stay one step ahead of hackers.

    Our ethical hacker course covers hands-on methods for securing networks against rogue access points and other wireless threats.


    Bonus: Tools You Can Use for Rogue AP Detection

    Here are some ethical hacking tools you can start using today:

    • Aircrack-ng: Great for analyzing wireless network vulnerabilities.
    • Wireshark: Excellent for capturing and analyzing network traffic.
    • Nmap: Learn how to scan a network with Nmap and identify unauthorized devices fast.

    At SpyWizards.com, we teach you TCP/IP basics for hackers so you can fully understand what your tools are doing under the hood.


    Conclusion

    Rogue access points represent a silent but critical threat to your network. Detecting and preventing them requires vigilance, education, and the right tools. By scanning regularly, securing your infrastructure, and conducting frequent penetration tests, you can significantly reduce your risk.

  • Role of VPNs in Secure Communication: A Must-Have for Modern Cybersecurity

    In todayโ€™s digital landscape, secure communication is more critical than ever. Whether youโ€™re a professional ethical hacker, a cybersecurity enthusiast, or simply someone who values online privacy, understanding the role of VPNs in secure communication is crucial. VPNs (Virtual Private Networks) offer a shield against cyber threats, safeguarding sensitive data and preserving anonymity across networks.

    Role of VPNs in Secure Communication: A Must-Have for Modern Cybersecurity

    Role of VPNs in Secure Communication: A Must-Have for Modern Cybersecurity

    At Spy Wizards, we believe that mastering cybersecurity tools like VPNs is essential, especially when exploring ethical hacking tools, network security penetration testing, and understanding wireless network vulnerabilities.

    What is a VPN and How Does It Work?

    A VPN, or Virtual Private Network, encrypts your internet connection and routes it through a secure server. This masks your IP address, making your online actions virtually untraceable. For cybersecurity professionals and those learning through an ethical hacker course, VPNs are a cornerstone in building a secure digital environment.

    By encrypting your data, VPNs ensure that hackers, ISPs, and even governments cannot easily intercept or monitor your online activities. This layer of encryption is particularly vital when working in penetration testing lab setups or scanning for vulnerabilities.

    Learn more about ethical hacking tutorials for beginners to start your journey into cybersecurity the right way.

    Why VPNs are Essential for Ethical Hackers and Cybersecurity Experts

    When diving into how to become an ethical hacker, youโ€™ll quickly realize that anonymity and security are your greatest assets. Hereโ€™s why VPNs are indispensable for ethical hackers:

    • Enhanced Privacy: VPNs mask your identity, protecting you during activities like network security penetration testing or while identifying wireless network vulnerabilities.
    • Secure Research: Many cybersecurity tasks involve visiting potentially risky websites. VPNs create a secure channel, ensuring your personal information remains safe.
    • Geo-Restriction Bypass: Ethical hackers often need access to resources blocked by regional restrictions. VPNs remove these barriers effectively.

    Explore Spy Wizardsโ€™ guide on how to scan a network with Nmap to expand your technical toolkit safely and efficiently.

    VPNs and the OSI Model in Network Security

    Understanding the OSI model in network security is crucial for grasping how VPNs function. VPNs primarily operate at the Network Layer (Layer 3), securing data transmission across open networks. As you set up your own penetration testing lab, itโ€™s vital to know how VPN encryption affects packet handling, routing, and traffic visibility across different OSI layers.

    Dive deeper into TCP/IP basics for hackers and learn how VPNs impact the fundamental building blocks of internet communication.

    Best Practices for Using VPNs for Secure Communication

    While VPNs are powerful tools, they must be used correctly to maximize their benefits. Here are some expert tips:

    1. Choose a Trusted VPN Provider: Not all VPNs are created equal. Opt for reputable services that offer strong encryption protocols like OpenVPN or WireGuard.
    2. Enable Kill Switch Features: A kill switch automatically disconnects you from the internet if the VPN connection drops, ensuring your IP remains hidden.
    3. Avoid Free VPNs: Free services often come with hidden costs, such as selling your data. Invest in a premium VPN for genuine protection.
    4. Combine VPNs with Other Ethical Hacking Tools: Use VPNs alongside firewalls, antivirus software, and encryption tools to build a robust cybersecurity framework.

    Interested in more tools? Visit Spy Wizards for top recommendations on ethical hacking tools and guides.

    VPNs and Wireless Network Vulnerabilities

    One of the major challenges cybersecurity experts face is mitigating wireless network vulnerabilities. VPNs add an essential layer of protection when connecting to unsecured public Wi-Fi networks. By encrypting your data, VPNs prevent common attacks like:

    • Man-in-the-Middle (MITM) attacks
    • Session hijacking
    • Evil twin attacks

    Setting up a VPN is often one of the first lessons taught in an ethical hacking tutorial for beginners, and for good reason. Itโ€™s a simple yet effective way to shield sensitive operations during penetration tests.

    VPNs and Ethical Hacking: Real-World Applications

    When learning how to become an ethical hacker, youโ€™ll find that VPNs are used extensively during:

    • Reconnaissance: Gathering information without leaving a trace.
    • Exploitation: Safely testing vulnerabilities without revealing your true IP.
    • Reporting: Sending vulnerability reports securely to clients or team leads.

    Building a professional skillset? Check out our ethical hacker course designed for hands-on learners!

    Conclusion: Why You Canโ€™t Afford to Ignore VPNs

    The role of VPNs in secure communication cannot be overstated. Whether youโ€™re securing personal communications, setting up a penetration testing lab setup, or scanning a corporate network, VPNs are indispensable for maintaining integrity, confidentiality, and security.

    At Spy Wizards, weโ€™re committed to helping you master cybersecurity fundamentals. Whether youโ€™re a seasoned pro or exploring the world of ethical hacking tutorials for beginners, investing time in understanding and utilizing VPNs will protect your digital footprint and elevate your skills.

  • Securing Wi-Fi Networks at Home and Work

    In todayโ€™s connected world, securing Wi-Fi networks at home and work is no longer optionalโ€”itโ€™s a necessity. Unprotected wireless networks can expose sensitive data, allow unauthorized access, and create severe cybersecurity vulnerabilities. Whether youโ€™re managing a small home network or a corporate system, understanding wireless network security is essential for keeping your information safe.

    Securing Wi-Fi Networks at Home and Work

    Securing Wi-Fi Networks at Home and Work

    At SpyWizards.com, we believe that the best defense is a strong offense. Letโ€™s walk through proven strategies, tools, and best practices to secure your wireless networks against evolving threats.

    Why Securing Wi-Fi Networks Matters

    Wireless networks are highly convenient but also incredibly vulnerable. Attackers can exploit wireless network vulnerabilities to intercept traffic, steal data, or gain unauthorized access to your devices.

    When networks are left unsecured:

    • Personal information can be stolen.
    • Corporate data breaches can occur.
    • Malware and ransomware infections increase.
    • Unauthorized users can drain network resources.

    Understanding network security penetration testing and common threats is the first step toward safeguarding your digital world.


    How to Secure Your Home Wi-Fi Network

    Protecting your home Wi-Fi network is simpler than you might think. Here are some essential tips:

    1. Change Default Settings

    Routers come with default network names (SSIDs) and passwords that are easy to guess. Change these immediately to unique, strong credentials.

    2. Use Strong Encryption

    Always enable WPA3 encryption. If WPA3 is not available, use WPA2. Avoid WEP, which is outdated and insecure.

    3. Enable Network Firewalls

    Your router has a built-in firewallโ€”make sure itโ€™s enabled. Firewalls help block malicious traffic before it reaches your devices.

    4. Set Up a Guest Network

    Isolate guests by creating a separate network. This protects your primary devices from potential threats.

    5. Regularly Update Firmware

    Manufacturers release firmware updates to fix vulnerabilities. Regularly update your router to stay protected.

    Learn more about ethical hacking tools and defensive strategies at SpyWizards.com.


    How to Secure Your Office Wi-Fi Network

    Corporate networks are often prime targets for hackers. Hereโ€™s how to keep your business network secure:

    1. Implement Network Segmentation

    Separate employee, guest, and critical infrastructure networks. This minimizes the risk if one segment gets compromised.

    2. Invest in Enterprise-Grade Security

    Use professional routers and firewalls designed for businesses. Configure them with advanced security features like VPNs and intrusion prevention systems.

    3. Conduct Regular Security Audits

    Hire professionals trained in network security penetration testing and ethical hacking to regularly evaluate and strengthen your defenses.

    If youโ€™re considering advancing your cybersecurity skills, explore our ethical hacker course and take the first step toward a career in protecting digital environments.


    Common Wireless Network Vulnerabilities

    Understanding vulnerabilities helps you better defend against them. Common Wi-Fi threats include:

    • Rogue Access Points: Unauthorized devices pretending to be legitimate access points.
    • Evil Twin Attacks: Fake networks tricking users into connecting.
    • Man-in-the-Middle (MITM) Attacks: Intercepting and altering communications between devices.
    • Packet Sniffing: Capturing data packets traveling across the network.

    For a detailed ethical hacking tutorial for beginners, check out our resources at SpyWizards.com.


    How to Test Your Wi-Fi Network Security

    Professional penetration testers use specialized tools to assess network vulnerabilities. Hereโ€™s a quick look:

    1. Perform Network Scans

    Learning how to scan a network with Nmap is a foundational skill in ethical hacking. Nmap reveals open ports, services, and potential vulnerabilities on a network.

    2. Understand the OSI Model

    Mastering the OSI model in network security helps you recognize how data travels through a network and where vulnerabilities can be exploited.

    3. Set Up a Penetration Testing Lab

    Create a secure environment for practicing cybersecurity techniques. A penetration testing lab setup allows safe experimentation with real-world hacking tools.

    Dive into TCP/IP basics for hackers and enhance your skills with hands-on practice through our comprehensive tutorials at SpyWizards.com.


    Advanced Tips for Wireless Network Security

    Securing Wi-Fi Networks at Home and Work
    • Use VPNs: Encrypt all data transmitted over your network.
    • Monitor Network Activity: Use monitoring software to detect unusual behavior.
    • Disable Remote Management: Unless necessary, disable remote access to your routerโ€™s settings.
    • Use MAC Address Filtering: Allow only specific devices to connect to your network.

    Conclusion

    Securing Wi-Fi networks at home and at work is crucial for protecting personal and corporate data. By understanding wireless network vulnerabilities, employing professional ethical hacking tools, and staying informed about cybersecurity best practices, you can dramatically reduce your risk of a breach.

    Ready to become a cybersecurity expert? Explore our ethical hacker course and access a free ethical hacking tutorial for beginners. Learn how to become an ethical hacker and defend networks like a pro!