Meta Description: Discover how to use Wireshark to analyze network traffic effectively. Learn ethical hacking tools, TCP/IP basics, and uncover wireless network vulnerabilities. Visit SpyWizards.com for tutorials, courses, and professional penetration testing insights.
Using Wireshark to Analyze Network Traffic
Are you ready to explore how network traffic analysis can bolster your cybersecurity strategy? Wireshark, a powerful open-source packet analyzer, is a must-have tool in every ethical hacker’s toolkit. Whether you’re setting up your own penetration testing lab or diving into the fundamentals of the OSI model in network security, mastering Wireshark is a game-changer.
In this comprehensive guide, we’ll walk you through how to use Wireshark to analyze network traffic, identify vulnerabilities, and sharpen your ethical hacking skills. For more tips, tools, and training, visit SpyWizards.com — your go-to resource for all things cybersecurity.
What is Wireshark?
Wireshark is a network protocol analyzer that lets you capture and interactively browse the traffic running on a computer network. It’s widely used for network troubleshooting, analysis, software and protocol development, and education.
From capturing live traffic to dissecting packet structures, Wireshark is essential for understanding TCP/IP basics for hackers and identifying wireless network vulnerabilities.
Ensure you have the right permissions, especially on Windows or macOS. For hands-on practice, consider a dedicated penetration testing lab setup, available in our ethical hacking tutorial for beginners.
Analyzing Packets with Wireshark
When you’re capturing traffic:
Use filters like http, tcp.port == 80, or ip.addr == 192.168.1.1 to isolate specific data.
Drill down into each packet layer to explore the OSI model in network security.
Understanding packet flows and anomalies helps during network security penetration testing, especially when identifying threats like ARP spoofing or DNS poisoning.
Common Use Cases for Ethical Hackers
Ethical hackers and network professionals use Wireshark to:
Perform reconnaissance in penetration testing labs
Diagnose suspicious activities like brute-force attacks
Monitor clear-text credentials in insecure protocols (e.g., FTP, Telnet)
Mastering this tool aligns with the skills taught in our ethical hacker course, perfect for beginners and pros alike.
Real-World Scenario: How to Scan a Network with Nmap and Analyze with Wireshark
Start with an Nmap scan:
nmap -sS -p- 192.168.1.1/24
Then, capture the same traffic using Wireshark to:
Wireshark is more than a packet sniffer—it’s a gateway to mastering network analysis and becoming an elite cybersecurity professional. Whether you’re exploring TCP/IP basics for hackers, tackling wireless network vulnerabilities, or preparing for a real-world network security penetration testing, Wireshark is your ally.
Ready to take the next step? Dive deeper with our exclusive ethical hacker course and expand your skillset today.
Use cybersecurity guidance only on accounts, devices, and networks you own or are clearly authorized to review. If you are dealing with account recovery, suspicious logins, device privacy concerns, or business security checks, document what happened, preserve alerts or recovery emails, and avoid sharing passwords, one-time codes, private keys, or financial details. Spy Wizards focuses on lawful support, ethical security review, privacy protection, and practical recovery steps that reduce risk without crossing consent boundaries.
In today’s digital era, ethical hacking has become a vital component of cybersecurity. But with great power comes great responsibility—and legal boundaries. If you’re intrigued by how ethical hackers operate and want to understand the legal framework behind their actions, this article is your complete guide.
Before signing any agreement, review the legal considerations when hiring a hacker, including authorization, scope, and documentation.
Whether you’re pursuing an ethical hacker course or exploring ethical hacking tools, it’s crucial to grasp the laws, certifications, and ethical codes that govern the field.
Table of Contents
What Is Ethical Hacking?
Ethical hacking, also known as white-hat hacking, involves legally breaking into systems to discover vulnerabilities before malicious hackers can exploit them. It’s an authorized practice that supports security enhancement and digital safety.
To become a professional in this field, start by learning the ethical hacking tutorial for beginners, which introduces you to penetration testing, vulnerability scanning, and foundational cybersecurity skills.
Why Legal Knowledge Matters for Ethical Hackers
Performing hacking activities—even with good intentions—can cross legal boundaries if not properly authorized. Understanding the law ensures ethical hackers stay within scope and avoid criminal prosecution.
Some legal concepts to be aware of include:
Unauthorized Access: Gaining entry into any system without permission is a criminal offense in many countries.
Data Privacy Laws: Laws like the GDPR in the EU and the CCPA in California regulate data usage and mandate breach disclosures.
Computer Fraud and Abuse Act (CFAA): In the U.S., this act criminalizes unauthorized system access—even attempts count.
Perfect for advanced users looking to master exploit development and real-world attack simulations.
Learn more about how to build your certification path with our in-depth ethical hacker course.
Setting Up a Legal Penetration Testing Lab
To practice ethically and legally, set up a local environment using a penetration testing lab setup. This helps you test tools and techniques safely, without risking unauthorized access.
Your lab should include:
Virtual machines (e.g., Kali Linux)
Targets like Metasploitable or DVWA
Scanning tools such as Nmap, Burp Suite, or Wireshark
Ensure you also understand the OSI model in network security and the TCP/IP basics for hackers to decode traffic and vulnerabilities effectively.
Wireless Networks and Legal Implications
Exploring wireless network vulnerabilities is a key part of ethical hacking. However, it’s illegal to intercept Wi-Fi signals or networks without permission—even for testing purposes.
Always conduct wireless testing within a controlled lab environment or with signed authorization from the organization.
Staying Compliant: Global Cybersecurity Laws
Different countries have unique cybersecurity laws. Here are a few key examples:
USA: Computer Fraud and Abuse Act (CFAA)
EU: General Data Protection Regulation (GDPR)
India: IT Act, 2000 (with amendments)
Canada: Personal Information Protection and Electronic Documents Act (PIPEDA)
To legally operate globally, ethical hackers must be familiar with international legal standards and practice responsible disclosure when vulnerabilities are found.
How to Become an Ethical Hacker—Legally and Effectively
Learn the Basics Understand systems, networks, and operating systems. Study the TCP/IP basics for hackers and OSI model to grasp how communication flows online.
Take a Course Enroll in a reliable ethical hacker course to gain structured knowledge and hands-on experience.
Get Certified Aim for industry-recognized certifications like CEH or OSCP.
Stay Legal Never test outside of authorized environments. Always document permission, scope, and testing procedures.
Final Thoughts: Ethics Over Everything
Ethical hacking isn’t just about knowing how to break into systems—it’s about protecting them and doing so legally and ethically. Respect for privacy, clear consent, and a deep understanding of cybersecurity law are all vital parts of being a responsible ethical hacker.
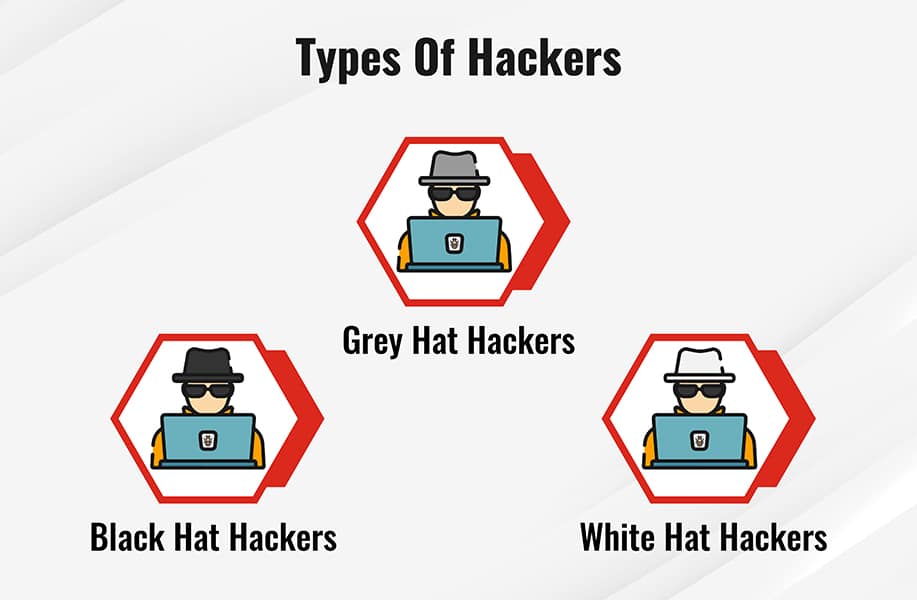
Quick answer: The 3 types of hackers are white hat hackers, black hat hackers, and gray hat hackers. White hats work legally to improve security, black hats break the law for profit or disruption, and gray hats operate in the middle, often without permission but not always with outright malicious intent.
If you need authorized help, look for white hat hackers for hire who work with written permission and clear reporting.
Updated April 2026
If you are trying to understand the 3 types of hackers, this guide breaks down the real differences in plain English. We will compare white hat vs black hat vs gray hat hackers, explain what each group does, and show why the distinction matters for businesses, students, and anyone researching cybersecurity.
This topic also matters commercially. If a company needs a security assessment, vulnerability review, or penetration test, it should work only with a white hat hacker or an authorized cybersecurity team. If you need the broader legal background first, read What Is Ethical Hacking? Responsibilities and Limitations.
Table of Contents
What Are the 3 Types of Hackers?
The most common way to classify hackers is by intent, authorization, and legal status:
White hat hackers: Authorized security professionals who test systems legally to improve defenses.
Black hat hackers: Criminal attackers who exploit systems for theft, extortion, fraud, or disruption.
Gray hat hackers: People who may find and disclose vulnerabilities without permission, even if they claim good intentions.
If you searched for what are 3 types of hackers or three types of hackers, this is the core answer. The rest of the page explains why those labels matter in practice.
White Hat Hackers: The Ethical Security Professionals
White hat hackers are cybersecurity professionals who work with clear permission. Their job is to identify weaknesses before criminals do. In a business setting, this usually means penetration testing, vulnerability validation, cloud security reviews, web application testing, wireless security assessments, or incident response support.
What makes a white hat different is not just skill. It is authorization, documentation, and scope. A legitimate white hat works under written rules of engagement, legal approval, and a defined objective. If you want to understand those boundaries better, see Rules of Engagement in Ethical Hacking and The Legal Side of Ethical Hacking.
What White Hat Hackers Usually Do
Test web applications, networks, mobile apps, and cloud systems with permission.
Document vulnerabilities, business impact, and remediation steps.
Help organizations reduce risk before attackers find the same weaknesses.
Support compliance programs, security audits, and internal defense planning.
Why Businesses Hire White Hat Hackers
This is the most commercially important part of the topic. Businesses do not hire “hackers” in the movie sense. They hire authorized professionals to:
Run a penetration test before launch.
Investigate signs of compromise.
Validate security controls after a major change.
Prepare for audits, insurance, or compliance reviews.
If your organization needs that kind of help, the right move is to work with a lawful security team, not a gray hat or black hat actor. You can start that conversation through the Spy Wizards contact page.
Black Hat Hackers: Illegal Attackers and Real-World Threats
Black hat hackers are the attackers most people picture when they hear the word hacker. They break into systems without permission and use that access for profit, espionage, fraud, sabotage, or extortion. Their methods vary, but their defining trait is simple: they operate outside the law and against the interests of the victim.
Black hats may target businesses, consumers, schools, healthcare providers, government systems, or financial platforms. Their goals can include credential theft, ransomware deployment, business email compromise, data resale, or service disruption.
Common Black Hat Objectives
Steal credentials, personal data, or financial records.
Deploy ransomware or other malware.
Exploit weak configurations and unpatched software.
Use phishing or social engineering to gain access.
The important trust point here is that people looking for security help should understand that a black hat is never a legitimate service provider. If a company or individual promises unauthorized access, guaranteed account takeovers, or secret system entry, that is a major warning sign, not a professional offering.
Gray Hat Hackers: The Legal and Ethical Middle Ground
Gray hat hackers sit between white hats and black hats. They may discover weaknesses and disclose them, but they often do it without authorization. That is why gray hat behavior is risky. A person may believe they are helping, but if they accessed or tested a system without permission, they can still create legal exposure for themselves and real operational risk for the target.
This is why many businesses do not want “good intentions” alone. They want contracts, scope, and a clear disclosure process. In modern cybersecurity, professionalism matters as much as technical ability.
Why Gray Hats Are Still Risky
No written permission from the target.
Possible violation of law, policy, or terms of service.
Can trigger incident response, downtime, or liability issues.
May expect payment or recognition after the fact.
If you are comparing the difference between a white-hat, grey-hat and black-hat hacker, the key difference is this: white hats have authorization, black hats have malicious intent, and gray hats often lack authorization even when they claim a constructive motive.
White Hat vs Black Hat vs Gray Hat: Side-by-Side Comparison
Type
Permission
Intent
Legal status
Business value
White hat
Yes
Protect and improve security
Legal when properly authorized
High
Black hat
No
Steal, extort, disrupt, or profit
Illegal
None
Gray hat
No or unclear
Mixed; may claim good intent
Legally risky
Unreliable
This comparison is the clearest answer for readers searching white hat vs black hat vs gray hat or white, black and grey hacking.
Which Type of Hacker Should a Business Hire?
A business should hire only a white hat hacker, ethical hacking firm, or authorized security consultant. That provider should be able to explain:
The testing scope.
The legal authorization required.
The methodology and reporting process.
The remediation support available after testing.
If you are researching this topic from a buyer’s perspective, the real commercial query is not “Which hacker should I hire?” It is “Which authorized security professional can legally test my systems and help me reduce risk?” That is a white hat use case, and it belongs inside formal cybersecurity services.
For readers moving from education to action, the next logical step is to understand the limits of lawful work in ethical hacking responsibilities and limitations, then reach out through Contact Us if you need a legitimate security discussion.
How to Become a White Hat Hacker
Many readers landing on this page are not buyers. They are students, career changers, and early-stage cybersecurity learners. For them, the most valuable direction is toward white hat work, not gray or black hat behavior.
A strong white hat path usually includes:
Learning networking, systems, and basic security concepts.
Practicing in legal labs and training environments.
Studying ethical hacking methods and reporting discipline.
Understanding law, compliance, and authorization.
Building hands-on experience with defensive and assessment tools.
Start with What Is Ethical Hacking?, then continue to laws and certifications. Those pages are a much better next step than generic homepage links because they match the search intent behind this article.
Why Understanding Hacker Types Matters for Rankings and Revenue
From an SEO and business perspective, this topic sits near the top of the funnel. People searching 3 types of hackers are usually in research mode, not ready to buy immediately. That means this page should do two jobs well:
Rank and earn clicks for the comparison query cluster.
Move readers deeper into white-hat, legal, and service-oriented pages.
That is why this article now emphasizes the commercial difference between learning about hackers and hiring authorized security help. The money is not in forcing an informational page to sound like a sales page. The money comes from matching intent first, then guiding qualified readers toward ethical security services.
FAQs About the 3 Types of Hackers
What are the 3 types of hackers? The 3 main types of hackers are white hat hackers, black hat hackers, and gray hat hackers. They are grouped by intent, permission, and legal status.
What is the difference between a white hat hacker and a black hat hacker? A white hat hacker has authorization and works to improve security. A black hat hacker has no authorization and attacks systems for criminal or harmful purposes.
Are gray hat hackers illegal? Gray hat behavior can still be illegal or contractually prohibited because the person often acts without permission, even if they claim they are helping.
Which type of hacker should a company hire? A company should hire only a white hat hacker or authorized cybersecurity team for legal assessments, testing, and remediation support.
Can a gray hat hacker become a white hat hacker? Yes. With proper authorization, training, and legal discipline, someone can move into professional white-hat security work.
Why do people search for white hat vs black hat vs gray hat? Most readers want a simple way to compare legality, intent, and risk. Businesses also use this distinction when deciding whether a service provider is trustworthy and lawful.
Final Takeaway
If you remember only one thing, remember this: white hats are authorized defenders, black hats are illegal attackers, and gray hats are risky because they operate without clear permission.
In a digital world brimming with cyber threats, ethical hacking stands out as a crucial line of defense. But what exactly is ethical hacking, and where does one draw the line between ethical and illegal intrusion?
Our main guide explains authorized ethical hacker services so you can separate authorized testing from risky requests.
This guide will walk you through what ethical hacking truly entails, its core responsibilities, and the boundaries that ethical hackers must never cross. Whether you’re just beginning your ethical hacking tutorial for beginners or looking to dive deeper into network security penetration testing, this post has you covered.
Table of Contents
What is Ethical Hacking?
Ethical hacking, also called “white-hat hacking,” is the authorized practice of bypassing system security to identify potential threats and vulnerabilities. Ethical hackers are cybersecurity professionals hired to simulate cyberattacks—legally—with the goal of improving digital defenses.
Unlike black-hat hackers, who exploit vulnerabilities for personal gain or malicious intent, ethical hackers help organizations fortify their systems against such attacks.
Looking to build your skills? Explore our expert-curated ethical hacking course to get started.
Key Responsibilities of Ethical Hackers
Ethical hackers follow a structured and professional approach when testing systems. Their responsibilities include:
1. Performing Penetration Testing
One of their primary roles is conducting penetration testing to evaluate the security of applications, systems, and networks. This includes simulating attacks to find security loopholes.
Knowledge of the OSI model in network security and TCP/IP basics for hackers is essential to understanding how data moves through systems and where weak points may exist.
As cybersecurity threats evolve, organizations must stay ahead of malicious actors. Ethical hackers help prevent data breaches, protect customer data, and maintain public trust.
Whether you’re testing a corporate firewall, uncovering wireless vulnerabilities, or probing your systems with Nmap, ethical hackers make the internet a safer place—one test at a time.
Final Thoughts
Ethical hacking isn’t just a career—it’s a responsibility. It demands deep knowledge, a strong moral compass, and a commitment to digital safety. If you’re passionate about cybersecurity, ethical hacking is your chance to be a hero in the shadows.
Want to learn more or need professional guidance? Visit us at SpyWizards.com for expert resources and ethical hacking tools.
In today’s digital age, monitoring phone activity is increasingly sought after for protecting loved ones or ensuring workplace productivity. OneSpy Reviews: Your Go-To Resource For Spying Solutions offers insights into OneSpy, a popular phone monitoring software, but its use raises ethical, legal, and technical questions. As of June 28, 2025, concerns about digital privacy and spyware risks are growing, with users seeking reliable tools to balance safety and trust in relationships or businesses. This article explores OneSpy’s features, ethical considerations, legal implications, and technical challenges, drawing from user reviews and cybersecurity perspectives. By understanding phone monitoring and leveraging ethical hacking, you can make informed decisions about using such tools responsibly. Let’s dive into OneSpy’s capabilities, risks, and alternatives to ensure mobile security and trust.
Ethical Considerations of Using OneSpy
Using phone monitoring software like OneSpy raises significant ethical questions, particularly around digital privacy and trust. OneSpy Reviews: Your Go-To Resource For Spying Solutions highlights both its benefits and ethical dilemmas.
Impact on Trust in Relationships
Monitoring a child’s or partner’s phone without consent can erode trust in relationships. OneSpy allows tracking of calls, messages, and social media, but secretive use may damage personal bonds. A Psychology Today article emphasizes that transparency is key to maintaining trust. Users must weigh the intent—such as ensuring a child’s safety—against potential privacy violations. Ethical hacking principles advocate for consent and transparency. Learn more about ethical approaches at ethical hacking services.
Responsible Use in Business Settings
In workplaces, OneSpy is used for employee tracking to boost productivity, but monitoring without clear policies can foster distrust. Reviews on sites like Trustpilot note OneSpy’s effectiveness for tracking employee devices but criticize its lack of transparency. Employers should establish clear monitoring policies to align with cybersecurity solutions and respect employee privacy. For guidance on ethical monitoring, visit data protection resources.
Legal Implications of Phone Monitoring
Using OneSpy or similar tools involves navigating complex legal landscapes. Unauthorized monitoring can violate data protection laws and lead to severe consequences.
Privacy Laws and Regulations
In the U.S., the Electronic Communications Privacy Act (ECPA) and state laws prohibit unauthorized interception of communications. The EU’s General Data Protection Regulation (GDPR) imposes strict rules on data collection, requiring explicit consent. A Harvard Law Review article notes that non-consensual monitoring can lead to fines or lawsuits. OneSpy’s use must comply with these laws, especially for employee tracking. Users should inform targets or seek legal advice to avoid violations. For professional compliance support, explore cybersecurity services.
Risks of Non-Consensual Monitoring
OneSpy reviews, such as those on Sitejabber, report mixed experiences, with some users facing legal disputes over unauthorized use. Non-consensual monitoring can lead to civil or criminal penalties, particularly if data is misused. Ethical hacking emphasizes legal compliance to protect users and targets. Consulting professionals can ensure adherence to data protection laws. Visit penetration testing services for legal cybersecurity solutions.
Technical Challenges of OneSpy
OneSpy’s features, like call recording and GPS tracking, are powerful but come with technical challenges that impact reliability and mobile security.
Installation and Compatibility Issues
OneSpy requires physical access to install on Android devices and often needs rooting, which can expose devices to spyware risks. Reviews on Trustpilot highlight difficulties with installation and compatibility, with some users reporting software failure after days. Rooting voids warranties and increases vulnerability to malware, as noted in a Kaspersky blog. Ensuring proper setup is critical for effective phone monitoring. For secure installation guidance, check cybersecurity tips.
Data Security and Reliability
OneSpy’s data collection raises concerns about how monitored data is stored and protected. Reviews on MouthShut mention system instability, with some users detecting the app on target devices. Poor encryption or server vulnerabilities could expose sensitive data to hackers. Ethical hacking can assess such risks, ensuring robust digital privacy. For vulnerability testing, explore Hacker01’s services.
Solutions and Alternatives to OneSpy
To address OneSpy’s limitations, consider alternatives and best practices for responsible phone monitoring while prioritizing digital privacy.
Communicate Openly: For parental or employee monitoring, discuss intentions to maintain trust in relationships. Transparency reduces ethical concerns.
Choose Reputable Alternatives: Apps like mSpy or FlexiSPY offer similar features with better customer support and reliability, per user reviews. Always verify compatibility and security.
Enable Two-Factor Authentication (2FA): Secure your monitoring account with 2FA to prevent unauthorized access to collected data.
Use Encrypted Platforms: Opt for tools with strong encryption to protect monitored data, reducing spyware risks.
Consult Legal Experts: Ensure compliance with data protection laws by consulting legal professionals before monitoring.
Test with Ethical Hacking: Use ethical hacking to assess monitoring apps for vulnerabilities, ensuring mobile security. Visit penetration testing services for assessments.
Explore Parental Control Apps: For kids, apps like Qustodio provide safer, consent-based monitoring with robust cybersecurity solutions.
The Role of Ethical Hacking in Phone Monitoring
Ethical hacking plays a vital role in evaluating tools like OneSpy, ensuring they meet mobile security standards. White-hat hackers simulate attacks to identify vulnerabilities in monitoring apps, such as weak encryption or data leaks. According to Hacker01, ethical hacking services are essential for protecting users from spyware risks.
For users, ethical hacking ensures compliance with data protection laws and builds trust by securing sensitive data. Penetration testing can verify OneSpy’s server security or assess alternative apps, enhancing cybersecurity solutions. By partnering with professionals, you can use monitoring tools responsibly while maintaining digital privacy. Explore ethical hacking services to secure your monitoring practices.
Conclusion
OneSpy Reviews: Your Go-To Resource For Spying Solutions highlights OneSpy’s capabilities for phone monitoring, but its ethical, legal, and technical challenges demand careful consideration. From eroding trust in relationships to risking data protection law violations, unauthorized use can have serious consequences. Technical issues like installation complexity and data security further complicate its reliability. By communicating openly, choosing reputable alternatives, and leveraging ethical hacking, you can monitor responsibly while prioritizing digital privacy. Explore Hacker01’s cybersecurity solutions to ensure safe and ethical monitoring practices. Take action today to balance safety, trust, and mobile security in your personal or professional life.
Related WhatsApp guide: If you are comparing monitoring tools for chat safety, also review our guide to WhatsApp monitoring apps for parents and legal account recovery.
mSpy Vs SpyBubble
Choosing the right phone monitoring app can be daunting, especially when comparing mSpy Vs Spybubble: Which App Is The Best. As of June 28, 2025, parents, employers, and individuals seeking to ensure digital privacy face increasing cyber threats, making reliable monitoring tools essential. Both mSpy and SpyBubble offer robust features for tracking calls, messages, and locations, but they differ in functionality, ethics, and security. These tools can protect children, monitor employees, or even strain trust in relationships if misused. This article compares mSpy and SpyBubble, exploring their ethical implications, legal considerations, technical capabilities, and alternatives. By understanding their strengths and spyware risks, you can make an informed choice. Let’s dive into the mSpy Vs Spybubble:Which App Is The Best debate to find the ideal cybersecurity solution for your needs.
Ethical Considerations in Phone Monitoring
Using apps like mSpy or SpyBubble raises ethical questions, particularly around digital privacy and trust. The mSpy Vs Spybubble: Which App Is The Best comparison must consider their impact on relationships and responsible use.
Impact on Trust and Relationships
Monitoring without consent can erode trust in relationships, whether between parents and children or partners. mSpy’s stealth mode allows discreet tracking of calls, texts, and social media, but secretive use may harm personal bonds. SpyBubble, while similar, is less comprehensive, limiting its intrusiveness but also its utility. A Psychology Today article stresses transparency to maintain trust. Ethical hacking advocates for consent-based monitoring to balance safety and privacy. Learn more at ethical hacking services.
Responsible Use in Workplaces
For employee tracking, both apps monitor company devices, but clear policies are essential to avoid distrust. mSpy’s user-friendly dashboard and broader social media coverage make it more effective, per Trustpilot reviews. SpyBubble’s simpler interface suits basic needs but lacks depth. Employers must communicate monitoring policies to align with cybersecurity solutions. Explore data protection resources for ethical guidelines.
Legal Implications of Monitoring Apps
The legality of using mSpy or SpyBubble hinges on consent and compliance with data protection laws, a critical factor in the mSpy Vs Spybubble: Which App Is The Best debate.
Privacy Regulations and Compliance
Unauthorized monitoring violates laws like the U.S. Electronic Communications Privacy Act (ECPA) and the EU’s General Data Protection Regulation (GDPR). A Harvard Law Review article notes that non-consensual tracking can lead to fines or lawsuits. mSpy emphasizes legal use for parental control or employee monitoring with consent, while SpyBubble’s limited documentation raises compliance concerns. Parents can monitor minors legally, but monitoring adults without permission is risky. For compliance support, visit cybersecurity services.
Risks of Non-Consensual Use
Non-consensual use of either app can lead to legal repercussions. mSpy’s history of data breaches, reported by TechCrunch in 2024, raises concerns about data security, though it now uses AES-256 encryption. SpyBubble’s lack of iOS support limits its risks but also its versatility. Ethical hacking can ensure legal and secure use. Check penetration testing services for secure monitoring solutions.
Technical Capabilities and Limitations
The technical strengths and weaknesses of mSpy and SpyBubble are pivotal in determining mSpy Vs Spybubble: Which App Is The Best for mobile security.
Feature Comparison
mSpy offers extensive features, including social media monitoring (WhatsApp, Snapchat, Instagram), keylogging, and screen recording, though some require rooting or jailbreaking, which increases spyware risks. SpyBubble supports call logs, texts, and limited social media (WhatsApp, Facebook) but lacks advanced features like email monitoring and works only on Android. mSpy’s cross-platform compatibility (Android, iOS) and intuitive dashboard make it more versatile, while SpyBubble’s simpler setup appeals to beginners.
Installation and Security Challenges
mSpy’s installation on Android requires disabling Google Play Protect, risking malware exposure, and iOS setups may need jailbreaking or iCloud credentials. SpyBubble’s Android-only installation is straightforward but less secure due to minimal encryption details. Both apps’ stealth modes raise digital privacy concerns if detected by anti-spyware tools. For secure setups, explore cybersecurity tips.
Solutions and Alternatives for Safe Monitoring
To address limitations in the mSpy Vs Spybubble: Which App Is The Best comparison, consider these best practices and alternatives for responsible phone monitoring.
Communicate Transparently: Inform minors or employees about monitoring to maintain trust in relationships and comply with data protection laws.
Use Strong Encryption: Choose apps with robust encryption, like mSpy’s AES-256, to minimize spyware risks.
Enable 2FA: Secure monitoring accounts with two-factor authentication to prevent unauthorized access.
Explore Alternatives: Apps like uMobix offer advanced social media monitoring, including real-time Instagram and TikTok tracking, surpassing both mSpy and SpyBubble. Qustodio provides comprehensive parental control with screen time limits and web filtering, ideal for families.
Regular Security Audits: Use ethical hacking to test app vulnerabilities, ensuring mobile security. Visit penetration testing services.
Check Local Laws: Verify legal requirements before monitoring to avoid violations of data protection laws.
The Role of Ethical Hacking in Monitoring Apps
Ethical hacking enhances the security of apps like mSpy and SpyBubble by identifying vulnerabilities before malicious actors exploit them. In the mSpy Vs Spybubble: Which App Is The Best debate, ethical hacking ensures safe use. White-hat hackers test for data leaks, weak encryption, or installation risks, critical given mSpy’s past breaches. These services help users comply with data protection laws and maintain digital privacy. For parents and employers, ethical hacking builds trust by securing monitored data. Learn how to secure monitoring apps at ethical hacking services.
Conclusion
The mSpy Vs Spybubble: Which App Is The Best debate hinges on your monitoring needs, ethical priorities, and mobile security requirements. mSpy excels with its comprehensive features, cross-platform support, and user-friendly dashboard, making it ideal for detailed phone monitoring. SpyBubble offers simplicity but lacks iOS compatibility and advanced tools. Both require careful use to avoid spyware risks and maintain trust in relationships. Alternatives like uMobix or Qustodio provide robust options for parental control or employee tracking. For secure and ethical monitoring, leverage ethical hacking services. Explore Hacker01’s cybersecurity solutions to choose the best monitoring app and protect your digital world responsibly.
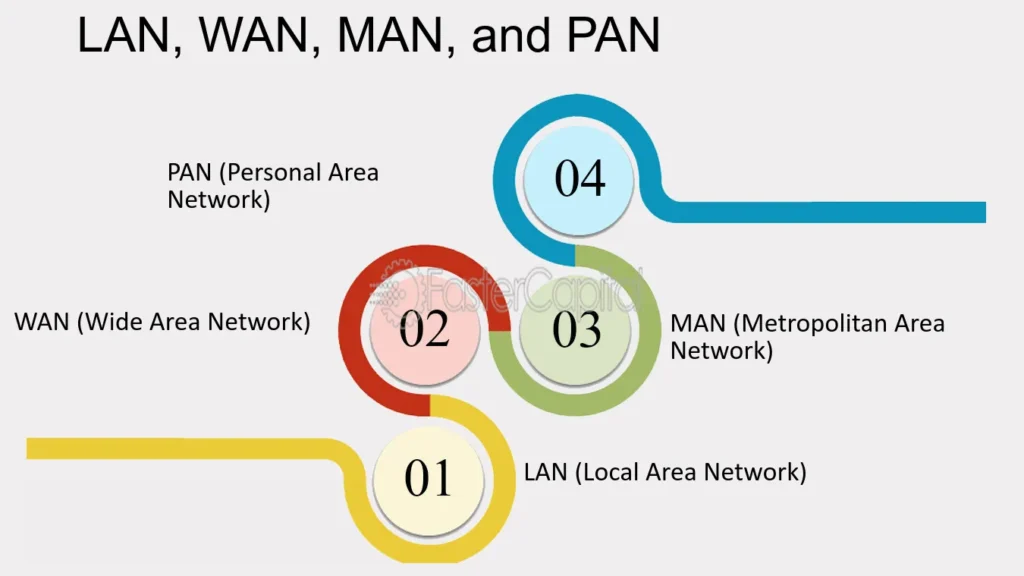
In this beginner-friendly guide, we’ll break down the basics of LANs, WANs, and MANs, show how they impact network security penetration testing, and introduce real-world tools and techniques used in ethical hacking.
Quick Tip: Want to kickstart your career in cybersecurity? Check out our ethical hacker course or dive into our free ethical hacking tutorial for beginners to get started.
What Is Network Architecture?
Network architecture refers to the design and structure of a computer network. It outlines how devices (like computers, servers, switches, and routers) are connected and communicate with each other.
A Local Area Network (LAN) connects computers and devices within a small geographic area, like an office, school, or home. LANs offer high-speed connections and are usually managed by a single organization.
Key Features of LAN:
Limited to a small area
High-speed data transfer
Typically uses Ethernet and Wi-Fi
Cost-effective
Interested in testing your own LAN for weaknesses? Learn how to scan a network with Nmap — one of the most powerful tools for ethical hackers.
LANs are where most penetration testing lab setups begin. You can simulate attacks, explore TCP/IP basics for hackers, and test various ethical hacking tools.
WAN: Wide Area Network
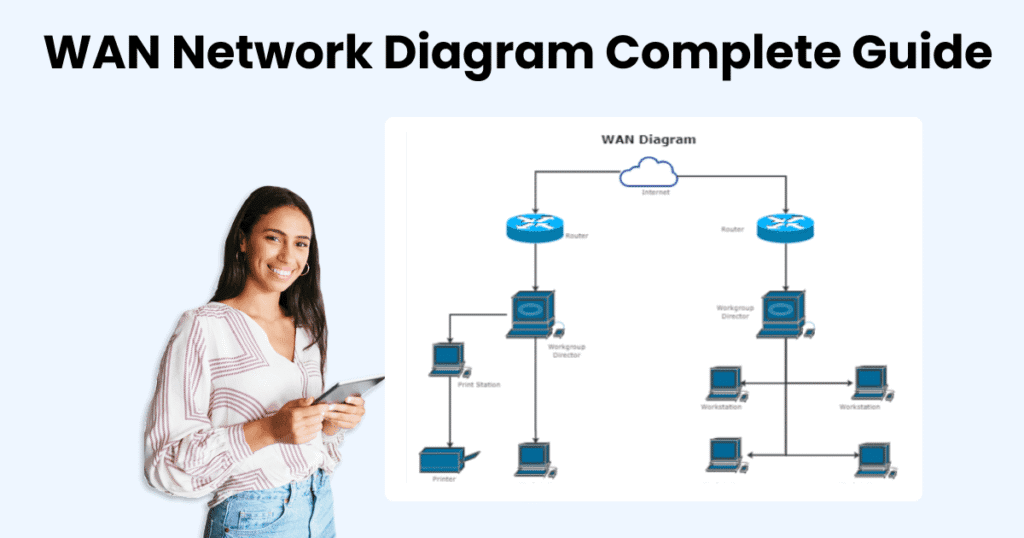
A Wide Area Network (WAN) spans large geographic distances and connects multiple LANs. The internet itself is the largest WAN in existence.
Key Features of WAN:
Covers large areas (cities, countries, continents)
Typically slower than LANs
Requires leased telecommunication lines
Uses routing and switching to manage traffic
Because WANs connect systems across vast distances, they’re a prime target for cyberattacks. This is where ethical hacking and network security penetration testing become critical.
MAN: Metropolitan Area Network
A Metropolitan Area Network (MAN) bridges the gap between LANs and WANs. It connects multiple LANs across a city or metropolitan area, often maintained by ISPs or large enterprises.
Key Features of MAN:
Spans cities or large campuses
Higher speed than WANs
Often used by governments and universities
A MAN offers more robust connectivity than a LAN and requires advanced security architecture to prevent intrusions—making it a great environment for ethical hackers to practice real-world scenarios.
Network Layers: OSI Model & TCP/IP
Understanding the OSI model in network security is vital when dealing with any type of network (LAN, WAN, or MAN). It helps ethical hackers pinpoint vulnerabilities at different layers.
OSI Layers at a Glance:
Physical – cables, switches
Data Link – MAC addresses
Network – IP routing
Transport – TCP/UDP
Session – connections
Presentation – encryption
Application – user interfaces
Pair this with TCP/IP basics for hackers, and you’re ready to dissect any network architecture. Ethical hackers often use Nmap, Wireshark, and Metasploit to probe these layers during penetration tests.
Ethical Hacking and Network Architecture
Why does network architecture matter in ethical hacking?
It gives insight into how data travels, where vulnerabilities may lie, and how to simulate attacks efficiently. A clear grasp of LAN, WAN, and MAN environments makes your testing more effective—and your defenses stronger.
Want to build your own hacking lab? Follow our guide on penetration testing lab setup to simulate network scenarios and test tools safely.
Common Vulnerabilities in LANs, WANs, and MANs
Network Type
Potential Vulnerabilities
LAN
Weak passwords, open ports
WAN
Insecure data transmission
MAN
Misconfigured routers and firewalls
To tackle these issues, ethical hackers use a variety of tools to simulate attacks, detect flaws, and suggest solutions. Explore our collection of ethical hacking tools to get started.
Final Thoughts
Whether you’re securing a corporate WAN, simulating attacks on a home LAN, or analyzing traffic on a city-wide MAN, understanding the fundamentals of network architecture is essential. It’s the backbone of everything in network security, penetration testing, and ethical hacking.
Want to learn more about the world of cybersecurity? Visit SpyWizards.com for guides, tools, and tutorials designed for ethical hackers at every level.
Key Takeaways:
LAN is perfect for localized, high-speed environments.
WAN connects distant locations and requires more complex security.
MAN bridges LANs and WANs over cities.
Understanding OSI layers and TCP/IP basics helps with network analysis.
Tools like Nmap are essential for scanning and mapping networks.
In the ever-evolving world of cybersecurity, staying ahead of threats is no small feat. Ethical hackers play a crucial role in identifying and fixing security loopholes before malicious hackers can exploit them. Whether you’re just diving into an ethical hacking tutorial for beginners or building your own penetration testing lab setup, mastering the right tools is essential.
This guide highlights the top ethical hacking tools every professional should know, with direct insight into how they apply to real-world scenarios. Ready to boost your skills and enhance your impact? Let’s explore the tools that make ethical hackers successful.
AI-assisted tools are a newer category alongside these established utilities. Our AI security-assistant guide explains their real capabilities, limits, and safe-use checks.
1. Nmap (Network Mapper)
Use Case: Network discovery and security auditing.
If you’re wondering how to scan a network with Nmap, this tool is your go-to. Nmap helps ethical hackers map out network infrastructures, find live hosts, open ports, and detect operating systems. It’s a cornerstone for network security penetration testing.
2. Wireshark
Use Case: Network protocol analysis.
Wireshark is an advanced packet analyzer that lets hackers inspect network traffic in real-time. It’s especially useful when assessing wireless network vulnerabilities. By examining data packets, ethical hackers can detect unauthorized traffic and analyze suspicious behavior.
3. Metasploit Framework
Use Case: Exploitation and penetration testing.
Metasploit is an essential part of any ethical hacker’s toolkit. It allows you to simulate real-world attacks to identify weaknesses in your target systems. This tool is often used in professional ethical hacker courses and is a must for setting up a practical penetration testing lab.
4. Burp Suite
Use Case: Web application security testing.
Burp Suite enables ethical hackers to intercept, modify, and replay web traffic. It’s crucial for identifying vulnerabilities like SQL injection, XSS, and insecure authentication methods. Anyone taking an ethical hacking course should become proficient with Burp Suite.
5. Aircrack-ng
Use Case: Wireless network security assessment.
Wireless networks are often vulnerable to attack. Aircrack-ng allows ethical hackers to crack WEP and WPA-PSK keys, revealing potential security flaws. Perfect for evaluating wireless network vulnerabilities and securing access points.
6. Hydra
Use Case: Password cracking.
Hydra is a brute-force tool for testing login credentials across numerous protocols, including SSH, FTP, and HTTP. It’s a favorite among hackers learning the ropes through an ethical hacking tutorial for beginners.
7. Nessus
Use Case: Vulnerability scanning.
Nessus automates the process of finding vulnerabilities across networks, systems, and apps. A powerful tool for auditors and those performing network security penetration testing, Nessus provides detailed reports on potential exposures.
Foundational Knowledge Tools: Know Your Layers
Before mastering these tools, it’s critical to understand the underlying frameworks:
OSI Model in Network Security: Understanding the seven layers helps identify where vulnerabilities reside and how data travels across a network.
TCP/IP Basics for Hackers: Grasping TCP/IP fundamentals ensures you know how network communication works, which is vital for successful exploits.
Final Thoughts: Becoming a Pro in Ethical Hacking
Mastering these tools is only the beginning. If you’re serious about leveling up, consider enrolling in a comprehensive ethical hacker course or exploring hands-on labs for penetration testing lab setup. Ethical hacking is not just a career—it’s a commitment to making the digital world safer.
Whether you’re building skills through self-study or training with experts, remember: the best ethical hackers are lifelong learners.
Explore more resources and in-depth guides at SpyWizards.com to stay updated on the latest in cybersecurity.
Keywords: ethical hacking tools, ethical hacker course, how to become an ethical hacker, network security penetration testing, wireless network vulnerabilities, ethical hacking tutorial for beginners, penetration testing lab setup, OSI model in network security, TCP/IP basics for hackers, how to scan a network with Nmap.
Are you exploring the path of ethical hacking? One of the first concepts every aspiring hacker must master is the TCP/IP protocol suite. Understanding TCP/IP fundamentals is not just about memorizing terms—it’s about unlocking the core communication structure of the internet. This guide will break down the TCP/IP basics for hackers while introducing tools, techniques, and concepts essential for network security penetration testing.
Whether you’re a cybersecurity student or someone looking for an ethical hacking tutorial for beginners, this post will serve as your starting point into the layered world of networking and digital security.
TCP/IP Fundamentals for Ethical Hackers
Table of Contents
What is TCP/IP and Why Should Ethical Hackers Care?
TCP/IP (Transmission Control Protocol/Internet Protocol) is the fundamental protocol suite used for data transmission across the internet. As an ethical hacker, you must understand how data travels between systems in order to detect, exploit, and patch vulnerabilities.
TCP/IP is foundational to:
Scanning networks for open ports
Performing packet sniffing and analysis
Launching penetration testing simulations
Detecting wireless network vulnerabilities
Understanding these layers equips you with the knowledge to dissect communication between clients and servers, detect unauthorized access, and strengthen defenses.
The Four Layers of the TCP/IP Model
The TCP/IP model is composed of four layers, each handling specific aspects of data transmission:
1. Application Layer
Handles high-level protocols like HTTP, FTP, DNS, and SMTP. Tools like Wireshark and Burp Suite, widely used in ethical hacking tools, operate here.
2. Transport Layer
Includes TCP and UDP. This layer ensures the reliable delivery of data. TCP manages the handshake process, which is a critical area for man-in-the-middle attacks.
3. Internet Layer
This layer includes IP addressing and routing protocols. Ethical hackers analyze IP packets here to understand network paths and identify potential entry points.
4. Network Access Layer
Focuses on hardware addressing and media. At this level, you’re analyzing MAC addresses, Ethernet frames, and dealing with packet injection during attacks.
TCP/IP vs. OSI Model in Network Security
While TCP/IP is more practical and widely implemented, understanding the OSI model in network security gives ethical hackers a granular understanding of communication systems.
The OSI model has seven layers, allowing for more detailed diagnostics and mapping attacks to specific network layers. Combining both models empowers you during penetration testing lab setup and vulnerability scanning.
Real-World TCP/IP Usage in Ethical Hacking
To truly grasp TCP/IP, practical experience is key. Here’s how it’s used in the field:
Packet Sniffing:
Using tools like Wireshark, ethical hackers monitor live TCP/IP traffic to find sensitive information or detect unencrypted transmissions.
Port Scanning:
Understanding TCP flags like SYN, ACK, and FIN is critical when using tools like Nmap to scan networks. These scans help identify open ports and services vulnerable to exploitation.
TCP Handshake Attacks:
Manipulating the 3-way handshake can lead to DoS attacks, session hijacking, or SYN flooding, all vital concepts during ethical hacker courses.
Setting Up a Penetration Testing Lab to Practice TCP/IP Attacks
Learning TCP/IP through theory isn’t enough. Set up a virtual lab using tools like:
hping3 – Used for custom packet crafting and firewall evasion.
To master these tools, consider enrolling in our ethical hacker course designed to guide you from beginner to pro.
Why TCP/IP Mastery Is Essential for Ethical Hackers
Learning TCP/IP isn’t just a prerequisite; it’s a continuous journey. Every packet, every port, and every protocol reveals something about your target. When you understand the flow of TCP/IP traffic, you understand the soul of the internet—making you better equipped to defend or ethically exploit systems.
Looking for the best resources on how to become an ethical hacker? Visit SpyWizards.com to get started with tutorials, tools, and expert training today.
Final Thoughts
Grasping TCP/IP fundamentals is like learning the grammar of the internet’s language. Whether you’re just starting out or brushing up your skills, building a strong foundation in TCP/IP prepares you for advanced topics like wireless network vulnerabilities, packet injection, proxy chaining, and more.
In the ever-evolving world of cybersecurity, understanding how hackers exploit network protocols is crucial. These communication rules are the building blocks of the internet, yet they can also become entry points for malicious activity. This article will explore the common network protocols used by hackers, their vulnerabilities, and how you can protect your network.
Updated February 2026
Common Network Protocols Used by Hackers
Whether you’re learning how to become an ethical hacker or just want to secure your systems, this knowledge is a must. Let’s dive in.
Table of Contents
What Are Network Protocols?
Network protocols are standardized rules that allow devices to communicate over a network. They ensure that data is transferred reliably and efficiently between endpoints. However, when misconfigured or left unsecured, these same protocols can be manipulated by hackers.
Top Network Protocols Exploited by Hackers
1. Transmission Control Protocol/Internet Protocol (TCP/IP)
The backbone of the internet, TCP/IP, is used in almost every online interaction. Unfortunately, this ubiquity makes it a favorite target for attackers. Hackers use it to perform:
Packet sniffing
Session hijacking
IP spoofing
Learning the TCP/IP basics for hackers is a crucial step in mastering network exploitation techniques.
Want to understand this better? Explore our detailed resources on ethical hacking tools.
2. HyperText Transfer Protocol (HTTP) and HTTPS
HTTP and HTTPS are protocols used to transfer web pages. When a site only uses HTTP (without the ‘S’ for secure), hackers can intercept data via:
Man-in-the-middle (MITM) attacks
Session fixation
Cross-site scripting (XSS)
Ethical hackers often analyze HTTP headers and cookies during network security penetration testing to detect vulnerabilities.
3. Simple Mail Transfer Protocol (SMTP)
SMTP is used for sending emails. Hackers exploit it to:
Send spam
Phish credentials
Distribute malware
Understanding email protocol exploitation is often included in any good ethical hacker course.
4. Domain Name System (DNS)
DNS translates domain names into IP addresses. Hackers exploit it using:
DNS poisoning
DNS tunneling
DNS amplification attacks
If you’re planning a penetration testing lab setup, be sure to include DNS analysis tools to simulate real-world attacks.
5. Dynamic Host Configuration Protocol (DHCP)
DHCP assigns IP addresses to devices. Attackers may manipulate it to:
FTP transmits files across networks but often lacks encryption. This makes it a target for:
Credential sniffing
Data interception
Brute force attacks
FTP-based attacks are frequently tested during network security penetration testing.
7. Address Resolution Protocol (ARP)
ARP is used to resolve IP addresses to MAC addresses. Hackers use it for:
ARP spoofing
MITM attacks
Network sniffing
An understanding of the OSI model in network security is key to defending against ARP-related attacks.
Wireless Network Vulnerabilities and Protocol Exploits
Wireless networks use protocols like WEP, WPA, and WPA2. While WEP is outdated and insecure, even WPA2 has its flaws. Common wireless attack strategies include:
Ethical hackers study and exploit these protocols in controlled environments to uncover security flaws before malicious actors do. By simulating attacks through penetration testing, they help businesses fortify their systems.
Final Thoughts: Stay Ahead with Ethical Hacking Skills
Understanding how hackers manipulate network protocols gives you the edge in cybersecurity. Whether you’re a beginner or an advanced learner, embracing ethical hacking techniques will strengthen your skills and protect your digital assets.
Browse our extensive library of guides, tools, and ethical hacker courses to start your journey today.
Ready to Master the Art of Network Security?
Visit SpyWizards.com for the best resources on ethical hacking tools, network security penetration testing, and expert guidance on how to become an ethical hacker.
Meta Description (for SEO – under 160 characters): Explore the top network protocols used by hackers, their vulnerabilities, and how ethical hackers use them to secure systems. Learn more at SpyWizards.com.


 Looking to build your skills? Explore our expert-curated
 Ready to dive in? Start with our
 Want to learn more or need professional guidance? Visit us at
 Want to understand this better? Explore our detailed resources on